GovRAMP Compliance Automation & Assessment Readiness
Table of Contents
ToggleAutomate GovRAMP readiness, evidence collection, control mapping, assessment workflows, remediation, and Continuous Monitoring with Continuum GRC.
Continuum GRC is a compliance automation platform for managing GovRAMP readiness, security controls, evidence collection, assessment workflows, POA&M remediation, and Continuous Monitoring across Core, Ready, Authorized, and other GovRAMP verification pathways.
Built for the GovRAMP Security Program
GovRAMP provides a standardized, risk-based approach for validating the security of cloud products using requirements based on NIST SP 800-53.
Continuum GRC helps cloud service providers operationalize GovRAMP by connecting security requirements, evidence, control implementation, findings, remediation, assessment activities, and Continuous Monitoring within one integrated GRC platform.
Organizations can use Continuum GRC to support the full GovRAMP lifecycle—from early readiness and Core Verification through Ready, Authorized, and Provisionally Authorized pathways.
GovRAMP currently recognizes multiple pathways including Security Snapshot, Progressing Security Snapshot, Core, Ready, Provisionally Authorized, and Authorized.
GovRAMP was formerly known as StateRAMP. StateRAMP remains the legal entity name, while GovRAMP is the program’s current operating name.
Built for the GovRAMP Security Program
GovRAMP provides a standardized, risk-based approach for validating the security of cloud products used by state, local, tribal, educational, and other public-sector organizations.
Continuum GRC helps cloud service providers operationalize GovRAMP by connecting security requirements, evidence, control implementation, findings, remediation, assessment activities, and Continuous Monitoring within one integrated GRC platform.
Organizations can use Continuum GRC to support the full GovRAMP lifecycle—from early readiness and Core Verification through Ready, Authorized, and Provisionally Authorized pathways.
GovRAMP currently recognizes multiple pathways including Security Snapshot, Progressing Security Snapshot, Core, Ready, Provisionally Authorized, and Authorized.
GovRAMP Verification Pathways
| GovRAMP Pathway | Purpose | Assessment Model | 3PAO Required |
|---|---|---|---|
| Security Snapshot | Provides an early view of a cloud service provider’s current security maturity and readiness. | Top 40 NIST security controls | No |
| Progressing Security Snapshot | Tracks improvement over time for providers actively strengthening their security posture. | Top 40 NIST security controls with recurring maturity review | No |
| Core Verification | Demonstrates verified foundational security maturity for providers seeking a recognized GovRAMP status. | 60 foundational NIST controls validated through the GovRAMP program | No |
| Ready Verification | Demonstrates readiness for broader public-sector use and progression toward full authorization. | 80 NIST controls with independent assessment | Yes |
| Provisionally Authorized | Confirms comprehensive security requirements are substantially met while limited dependencies or conditions remain. | Comprehensive assessment of 300+ controls | Yes |
| Authorized | Represents GovRAMP’s highest verification status for cloud service providers meeting comprehensive security requirements. | Comprehensive independent assessment of 300+ controls | Yes |
GovRAMP currently describes Core as 60 foundational controls, Ready as 80 controls, and Authorized/Provisional as 300+ controls.
How Continuum GRC Supports GovRAMP
| GovRAMP Area | Continuum GRC Support |
|---|---|
| Framework & Control Management | Centralize GovRAMP requirements, NIST SP 800-53 controls, control owners, implementation status, evidence, and assessment information. |
| Automated Evidence Collection | Collect and associate evidence through supported APIs, integrations, automation workflows, system-generated reports, and file repositories. |
| Assessment Readiness | Identify control gaps, missing evidence, incomplete requirements, and readiness issues before GovRAMP verification or independent assessment. |
| 3PAO Assessment Support | Organize assessment evidence, test results, findings, remediation history, and supporting documentation for independent GovRAMP assessment activities. |
| POA&M Management | Track findings, corrective actions, responsible owners, due dates, remediation progress, supporting evidence, and closure status. |
| Continuous Monitoring | Maintain recurring evidence, vulnerability information, changes, findings, remediation activities, and required monitoring workflows. |
| GovRAMP Verification Pathways | Support readiness and evidence management across Security Snapshot, Progressing Snapshot, Core, Ready, Provisionally Authorized, and Authorized pathways. |
| FedRAMP Evidence Reuse | Map and reuse applicable FedRAMP evidence, control information, and assessment artifacts against corresponding GovRAMP requirements where appropriate. |
| Cross-Framework Mapping | Reuse applicable controls and evidence across GovRAMP, FedRAMP, NIST, CMMC, ISO, SOC 2, and other mapped frameworks. |
| AI-Assisted Compliance with AITAMBot™ | Analyze compliance information, locate evidence, identify gaps, surface requirements needing attention, and assist with readiness and reporting workflows. |
| Dashboards & Reporting | Track verification readiness, control status, evidence health, findings, remediation progress, assessment activity, and Continuous Monitoring in real time. |
Turn GovRAMP Compliance Into an Ongoing Workflow
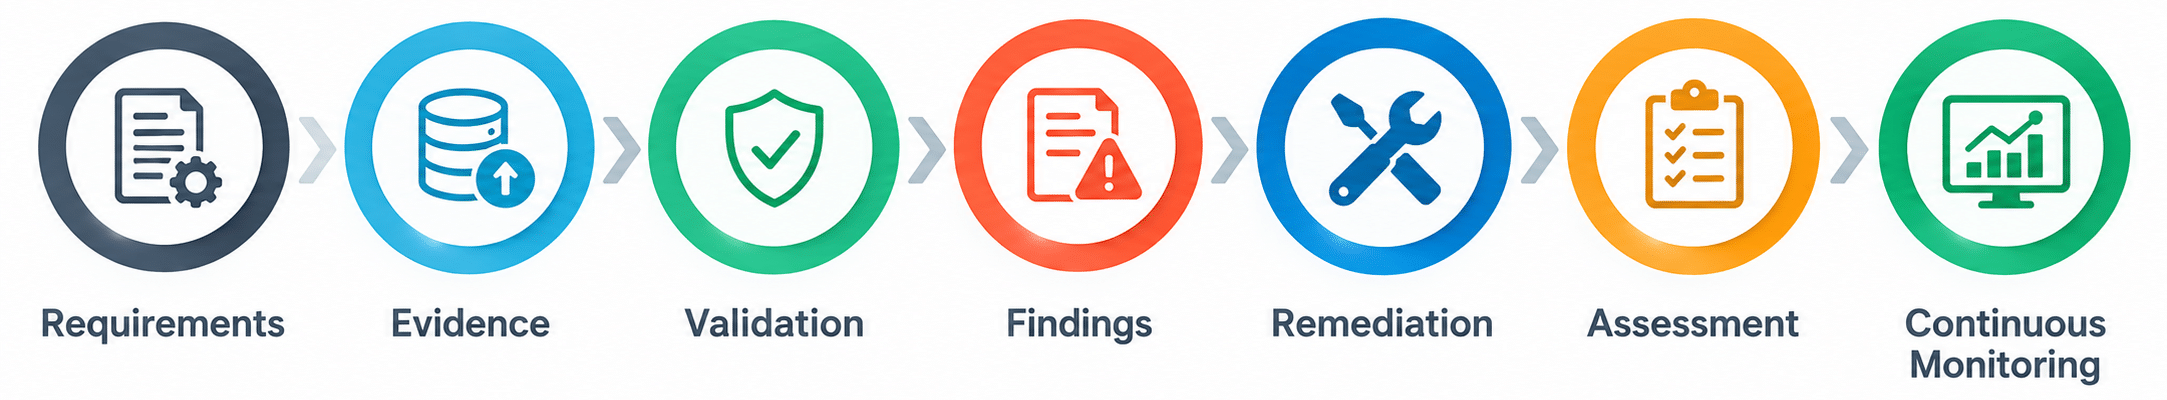
Continuum GRC transforms GovRAMP from a document-heavy assessment exercise into a structured, evidence-driven compliance lifecycle.
Automated GovRAMP Evidence Collection
GovRAMP readiness becomes difficult when security evidence is spread across spreadsheets, ticketing systems, cloud platforms, document repositories, and email.
Continuum GRC helps replace repetitive evidence-gathering activities with audit and compliance automation supported by APIs, integrations and automation workflows, system-generated reports, file repositories, and other connected data sources.
Evidence can be associated directly with applicable GovRAMP and NIST requirements so compliance teams can quickly identify:
- Missing evidence
- Stale evidence
- Incomplete controls
- Failed tests
- Open findings
- Remediation requiring attention
- Items requiring assessor review
AI-Assisted GovRAMP Compliance with AITAMBot™
AITAMBot™ helps compliance teams reduce manual review and preparation work by analyzing compliance information, locating evidence, identifying gaps, surfacing requirements requiring attention, and assisting with reporting.
AITAMBot can help:
- Find missing or outdated evidence
- Identify incomplete controls
- Surface findings requiring remediation
- Analyze readiness information
- Assist with assessment preparation
- Support report generation
- Query GovRAMP compliance information using natural language
AITAMBot™ works alongside compliance professionals and assessors rather than replacing required independent judgment, assessment, or validation.
Learn more about Continuum GRC's AI-powered compliance automation.
| Area | Core | Ready | Authorized / Provisional |
|---|---|---|---|
| Primary Purpose | Demonstrates verified foundational security maturity. | Demonstrates readiness for broader public-sector use and progression toward authorization. | Demonstrates comprehensive implementation of applicable GovRAMP security requirements. |
| Security Controls | 60 foundational controls | 80 controls | 300+ controls |
| Independent 3PAO Assessment | No | Yes | Yes |
| GovRAMP Validation | GovRAMP PMO validation | GovRAMP review following independent assessment | GovRAMP review following comprehensive independent assessment |
| Continuous Monitoring | Quarterly | Monthly | Monthly |
| Independent Annual Assessment | Not a full annual 3PAO assessment | Yes | Yes |
| Assessment Depth | Foundational security controls and evidence. | Expanded control set independently assessed for readiness. | Comprehensive independent assessment of the applicable GovRAMP security baseline. |
| Best Suited For | Providers establishing independently recognized foundational security maturity. | Providers preparing for broader government adoption or progressing toward authorization. | Providers seeking comprehensive GovRAMP verification for public-sector customers. |
| Continuum GRC Support | Control mapping, evidence management, readiness tracking, remediation, and quarterly monitoring. | Assessment readiness, evidence organization, 3PAO support, findings management, remediation, and monthly monitoring. | Comprehensive assessment workflows, evidence management, POA&M, remediation, reporting, and ongoing Continuous Monitoring. |
Reuse Existing FedRAMP Work
Organizations managing both programs can use Continuum GRC's FedRAMP compliance automation alongside GovRAMP workflows to map applicable controls, evidence, assessment information, and Continuous Monitoring activities across both programs.
GovRAMP allows providers with existing federal security documentation to reuse applicable work through its Fast Track process.
Existing materials can include items such as:
- Readiness Assessment Reports
- Security Assessment Reports
- Continuous Monitoring documentation
Continuum GRC helps organizations map and reuse existing FedRAMP evidence and documentation against applicable GovRAMP requirements, reducing unnecessary duplication and helping accelerate readiness.
GovRAMP explicitly supports reuse of existing federal security work through Fast Track.
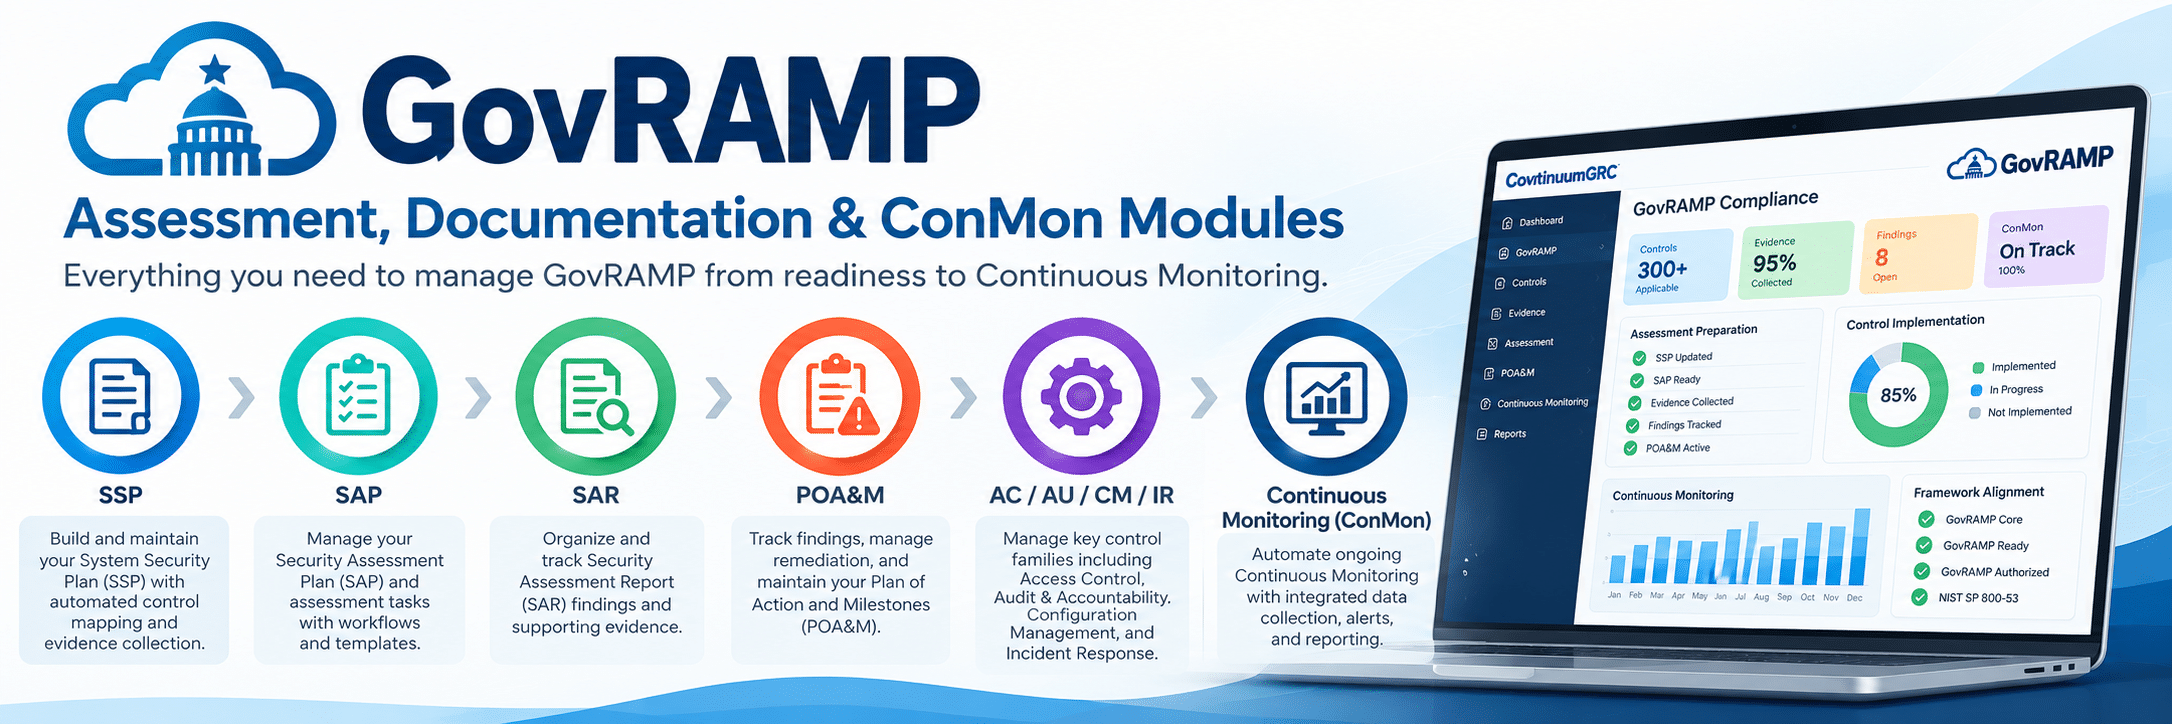
GovRAMP Assessment, Documentation & ConMon Modules
Continuum GRC provides GovRAMP CSP and 3PAO modules as part of its library of 100+ supported compliance frameworks.
Modules include:
CSP Bundle
- Security Snapshot
- GovRAMP Core
- System Security Plan (SSP) High-Moderate-Low
- System Security Plan (SSP)
- Security Assessment Report (SAR)
- Security Assessment Plan (SAP)
- Plan of Action and Milestones (POA&M)
- Customer Responsibility Matrix
- Electronic Authentication (E-Authentication) Plan
- Privacy Impact Assessment (PIA)
- Rules of Behavior (RoB)
- Information System Contingency Plan (ISCP)
- CIS for SSP Low, Moderate, or High Baselines
- Integrated Inventory Workbook
- Information System Security Policies and Procedures
- Configuration Management (CM) Plan
- Control Implementation Summary (CIS)
- CIS Worksheet
- IT Contingency Plan (CP)
- Incident Response Plan (IRP)
- Rules of Behavior (ROB)
- AC Access Control
- AT Awareness and Training
- AU Audit and Accountability
- CA Certification, Accreditation, and Security Assessment
- CM Configuration Management
- CP Contingency Planning
- IA Identification and Authentication
- IR Incident Response
- MA Maintenance
- MP Media Protection
- PE Physical and Environmental Protection
- PL Planning
- PS Personnel Security
- RA Risk Assessment
- SA System and Services Acquisition
- SC System and Communications Protection
- SI System and Information Integrity
- PM Project Management
3PAO Module Bundle includes:
- Security Assessment Report (SAR)
- Security Assessment Plan (SAP)
- SAR Risk Exposure Table (RET)
- SAR Moderate Security Requirements Traceability Matrix
- Annual Assessment Controls Selection Worksheet
ConMon
- Continuous Monitoring Activities & Deliverables: Continuous
- Continuous Monitoring Activities & Deliverables: Weekly
- Continuous Monitoring Activities & Deliverables: 10 days
- Continuous Monitoring Activities & Deliverables: Monthly
- Continuous Monitoring Activities & Deliverables: 60 days
- Continuous Monitoring Activities & Deliverables: Quarterly (90 days)
- Continuous Monitoring Activities & Deliverables: Annual
- Continuous Monitoring Activities & Deliverables: Every 2 years
- Continuous Monitoring Activities & Deliverables: Every 3 years
- Continuous Monitoring Activities & Deliverables: Every 5 years
- StateRAMP Significant Change Request Form
- StateRAMP Significant Change Request Form: Attachment A
Policies and Procedures
- AC – Access Control Policy
- AC – Access Control Procedure
- AT – Awareness & Training Policy
- AT – Awareness & Training Procedure
- AU – Audit & Accountability Policy
- AU – Audit & Accountability Procedure
- CA – Security Assessment and Authorization Policy
- CA – Security Assessment and Authorization Procedure
- CM – Configuration Management Policy
- CM – Configuration Management Procedure
- CP – Contingency Planning Policy
- CP – Contingency Planning Procedure
- IA – Identification & Authentication Policy
- IA – Identification & Authentication Procedure
- IR – Incident Response Policy
- IR – Incident Response Procedure
- MA – Maintenance Policy
- MA – Maintenance Procedure
- MP – Media Protection Policy
- MP – Media Protection Procedure
- PE – Physical & Environmental Policy
- PE – Physical & Environmental Procedure
- PL – Planning Policy
- PL – Planning Procedure
- PS – Personnel Policy
- PS – Personnel Procedure
- RA – Risk Assessment Policy
- RA – Risk Assessment Procedure
- SA – System & Services Acquisition Policy
- SA – System & Services Acquisition Procedure
- SC – System & Communications Protection Policy
- SC – System & Communications Protection Procedure
- SI – System & Information Integrity Policy
- SI – System & Information Integrity Procedure
Frequently Asked Questions
What is GovRAMP?
GovRAMP is a standardized cybersecurity verification program for cloud service providers serving state, local, tribal, educational, and other public-sector organizations. Based on NIST security requirements, GovRAMP provides multiple verification pathways that allow cloud providers to demonstrate increasing levels of security maturity, independent assessment, and ongoing compliance.
Is GovRAMP the same as StateRAMP?
GovRAMP is the current operating name of the program formerly known as StateRAMP. The organization announced the GovRAMP rebrand in 2025 to better reflect its broader public-sector mission. StateRAMP remains the legal entity name, while GovRAMP is the name used for the security program.
Who needs GovRAMP verification?
Cloud service providers that want to offer cloud products or services to participating state, local, tribal, educational, and other public-sector organizations may need or benefit from GovRAMP verification. The appropriate verification pathway depends on customer requirements, the provider's security maturity, and the level of assurance required.
What are the GovRAMP verification pathways?
GovRAMP provides several pathways for organizations at different stages of security maturity: Security Snapshot, Progressing Security Snapshot, Core, Ready, Provisionally Authorized, and Authorized. These pathways range from an initial assessment of security maturity to comprehensive independent assessment and ongoing Continuous Monitoring.
What is GovRAMP Core Verification?
GovRAMP Core is a foundational verification pathway based on 60 security controls. It allows cloud service providers to demonstrate verified implementation of essential security practices without completing the comprehensive independent assessment required for Ready or Authorized status. Core also includes ongoing monitoring requirements.
What is GovRAMP Ready?
GovRAMP Ready demonstrates that a cloud service provider has met an expanded set of security requirements and successfully completed the applicable independent assessment process. Ready includes 80 security controls and requires assessment by an approved Third-Party Assessment Organization (3PAO).
What is the difference between GovRAMP Ready and Authorized?
Ready demonstrates that a provider has successfully addressed an intermediate set of GovRAMP requirements and undergone independent assessment. Authorized represents a more comprehensive level of assurance involving the applicable GovRAMP security baseline, 300+ controls, independent assessment, and ongoing Continuous Monitoring. Provisionally Authorized provides a related pathway where applicable program conditions remain.
When is a 3PAO required for GovRAMP?
A 3PAO is not required for Security Snapshot, Progressing Security Snapshot, or Core Verification. An approved independent 3PAO is required for GovRAMP Ready and for Authorized or Provisionally Authorized verification pathways.
What does a GovRAMP 3PAO do?
A GovRAMP 3PAO independently evaluates whether a cloud service provider has implemented applicable security requirements and whether those controls operate as required. Assessment activities can include documentation review, evidence examination, interviews, technical testing, identification of findings, and preparation of required assessment results.
Does Continuum GRC replace a GovRAMP 3PAO?
No. Continuum GRC helps automate readiness, control management, evidence collection, remediation, assessment preparation, and Continuous Monitoring, but it does not replace required independent 3PAO judgment or assessment. AITAMBot™ can assist with evidence analysis and readiness activities while required independent assessment remains the responsibility of the approved assessor.
How does Continuum GRC automate GovRAMP compliance?
Continuum GRC centralizes GovRAMP requirements, NIST controls, evidence, control ownership, assessment activities, findings, remediation, POA&M information, and Continuous Monitoring within one platform. Integrations and automation workflows can reduce repetitive evidence collection while dashboards help teams identify missing evidence, incomplete controls, open findings, and requirements needing attention.
How does AITAMBot™ support GovRAMP compliance?
AITAMBot™ provides AI-assisted compliance analysis within Continuum GRC. It can help locate evidence, identify gaps, surface incomplete or potentially insufficient compliance information, assist with readiness analysis, identify remediation priorities, and support reporting. AITAMBot works alongside compliance professionals and assessors rather than replacing required independent judgment, assessment, or validation.
Can Continuum GRC automate GovRAMP evidence collection?
Yes. Continuum GRC can collect and organize evidence through supported APIs, integrations, automation workflows, system-generated reports, file repositories, and other connected data sources. Evidence can then be associated with applicable GovRAMP and NIST requirements, helping reduce repetitive manual evidence gathering.
What is GovRAMP Continuous Monitoring?
Continuous Monitoring is the ongoing process of maintaining visibility into a cloud service provider's security posture after verification. Depending on the applicable GovRAMP pathway, activities can include recurring vulnerability information, security evidence, control monitoring, findings, remediation, changes, and required reporting.
How often is GovRAMP Continuous Monitoring required?
The monitoring frequency depends on the verification pathway. GovRAMP Core uses quarterly monitoring, while Ready, Authorized, and Provisionally Authorized pathways have monthly Continuous Monitoring requirements. Providers should follow the current requirements associated with their specific GovRAMP status.
Can FedRAMP evidence be reused for GovRAMP?
Yes, where applicable. GovRAMP supports reuse of qualifying federal security work through mechanisms such as its Fast Track process. Existing FedRAMP documentation, assessment information, security evidence, and Continuous Monitoring materials may help reduce duplicated work when they satisfy corresponding GovRAMP requirements.
How does Continuum GRC help organizations reuse FedRAMP evidence for GovRAMP?
Continuum GRC maps requirements and evidence across compliance frameworks, allowing applicable FedRAMP controls, evidence, documentation, and assessment information to be associated with corresponding GovRAMP requirements. This can reduce unnecessary duplicate evidence requests while preserving traceability to each framework's specific requirements.
Does GovRAMP use NIST SP 800-53?
GovRAMP's security requirements are based on NIST security controls and use a risk-based approach derived from NIST SP 800-53. The number and scope of applicable controls vary according to the GovRAMP verification pathway and security baseline.
What is a GovRAMP POA&M?
A Plan of Action and Milestones (POA&M) documents identified security weaknesses and the actions planned to remediate them. Continuum GRC can help organizations manage findings, remediation owners, milestones, due dates, supporting evidence, status, and closure activities within the broader GovRAMP compliance workflow.
How long does GovRAMP verification take?
There is no single timeline that applies to every provider. The duration depends on the selected verification pathway, system scope and complexity, existing security maturity, documentation quality, evidence availability, remediation requirements, and assessment readiness. Automating evidence management and identifying gaps before formal assessment can help reduce avoidable delays.
Can Continuum GRC support both GovRAMP and FedRAMP?
Yes. Continuum GRC supports both GovRAMP and FedRAMP compliance workflows and can map applicable requirements and evidence across the frameworks. Organizations pursuing both programs can use cross-framework mapping and evidence reuse to reduce duplicated compliance work while maintaining framework-specific requirements, assessment activities, and reporting.
What is the best way to prepare for a GovRAMP assessment?
Begin by determining the appropriate GovRAMP verification pathway, defining the system scope, mapping applicable security requirements, identifying control owners, collecting current evidence, performing a readiness assessment, and remediating identified gaps before independent assessment. Continuum GRC helps manage these activities as a connected workflow rather than as separate spreadsheets, documents, and evidence requests
Contact us using the form below or calling us at 1-888-896-6207 for assistance.
AmWhat Continuum GRC Research Shows
In Continuum GRC’s 2026 Compliance Operations Benchmark Report, FedRAMP/StateRAMP programs represented 22% of the 275-program dataset. Across all programs, 42% used continuous or monthly control testing on critical controls and the median finding closure time was 38 days.
GovRAMP Compliance Platform Comparison – 2026
Compare Continuum GRC with other compliance platforms for GovRAMP readiness, evidence automation, assessment support, remediation, Continuous Monitoring, and multi-framework compliance management.
| GovRAMP Capability | Continuum GRC | Drata | Secureframe | Vanta | PreVeil |
|---|---|---|---|---|---|
| GovRAMP Compliance Management | ✅ Yes | Verify Current Offering | ✅ Yes | Verify Current Offering | Not Confirmed |
| GovRAMP Core Support | ✅ Yes | Verify Current Offering | ✅ Yes | Verify Current Offering | Not Confirmed |
| GovRAMP Ready / Authorized Workflow Support | ✅ Yes | Verify Current Offering | Verify Current Offering | Verify Current Offering | Not Confirmed |
| NIST SP 800-53 / GovRAMP Mapping | ✅ Yes | ✅ NIST 800-53 | ✅ Yes | Verify GovRAMP Mapping | Not Confirmed |
| Automated Evidence Collection | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Limited / Not Core GRC Function |
| GovRAMP Assessment Readiness | ✅ Yes | Verify Current Offering | ✅ Yes | Verify Current Offering | Not Confirmed |
| Integrated Independent Assessment Option | ✅ Available Through Accredited Assessment Organization | Partner / External Assessor | Partner / External Assessor | Partner / External Assessor | Partner / External Assessor |
| POA&M Management & Remediation Tracking | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Not Confirmed |
| Continuous Monitoring & Alerts | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Not Confirmed |
| Cross-Framework Evidence Reuse | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Not Confirmed |
| FedRAMP + GovRAMP Management | ✅ Yes | Verify GovRAMP Offering | ✅ Yes | Verify GovRAMP Offering | Not Confirmed |
| Custom Framework Creation | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Not Core Platform Function |
| AI-Assisted Compliance Analysis | ✅ AITAMBot™ | ✅ AI Capabilities | ✅ Secureframe AI | ✅ Vanta AI | Not Confirmed |
| Dedicated AI Auditor | ✅ AITAMBot™ | Not Confirmed | Not Confirmed | Not Confirmed | Not Confirmed |
| Real-Time Compliance Dashboard | ✅ Yes | ✅ Yes | ✅ Yes | ✅ Yes | Not Core GRC Function |
| Free 14-Day Trial – No Credit Card | ✅ Yes | Check Current Offer | Check Current Offer | Check Current Offer | Check Current Offer |
| Free GovRAMP Readiness Tools | ✅ Free GovRAMP Modules + AITAMBot™ | Check Current Offer | Check Current Offer | Check Current Offer | Not Confirmed |
Comparison note: Product capabilities and vendor offerings change frequently. Competitor information is based on publicly available information and should be confirmed directly with each provider. “Not Confirmed” indicates that the capability was not confirmed from current public product documentation reviewed for this comparison.