FedRAMP 20x Compliance Automation & KSI Management
Table of Contents
ToggleBuilt for the FedRAMP 20x Model
FedRAMP 20x fundamentally changes how cloud security is demonstrated. Instead of relying primarily on static narratives and periodic assessment activities, 20x emphasizes measurable security outcomes, machine-readable information, automation, persistent validation, and reusable evidence.
FedRAMP specifically describes KSIs as an abstraction of NIST SP 800-53 requirements designed around security capabilities that can frequently be determined from technical configurations and expressed as clear validation results.
Turn FedRAMP Requirements Into an Automated Compliance Lifecycle
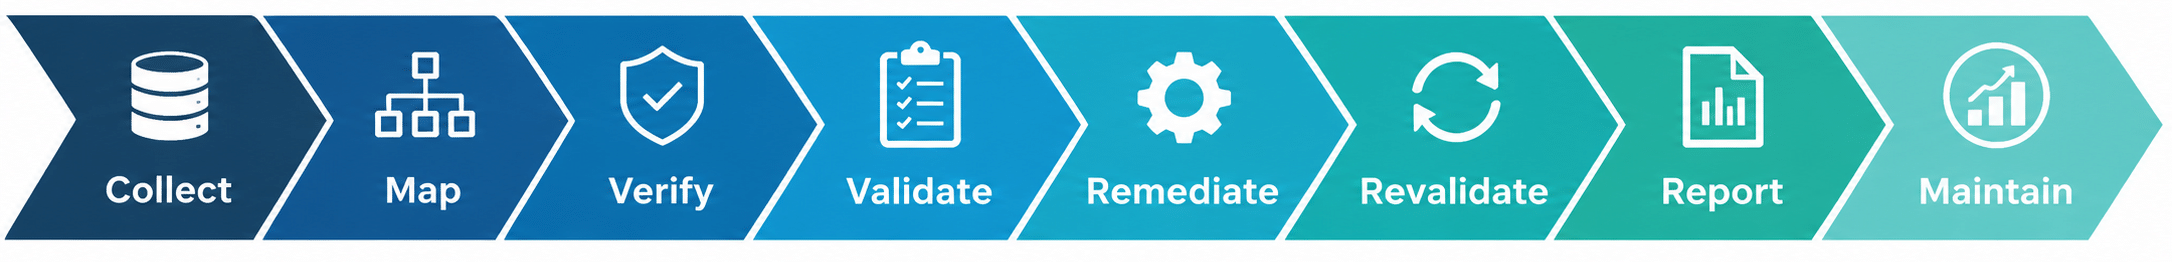
Continuum GRC helps organizations move beyond managing FedRAMP as a collection of documents and instead manage compliance as an ongoing, evidence-driven security process.
Automate FedRAMP 20x Readiness, KSI Validation, Evidence Collection & Ongoing Certification
Continuum GRC helps cloud service providers operationalize FedRAMP 20x by connecting Key Security Indicators (KSIs), automated evidence collection, persistent verification and validation, Security Decision Records, findings, remediation, independent assessment readiness, and Ongoing Certification within one integrated GRC platform.
Support both FedRAMP 20x and traditional FedRAMP Rev. 5 requirements while transitioning from document-intensive, point-in-time compliance toward measurable, continuously maintained security assurance.
FedRAMP 20x vs. Rev. 5 at a Glance
| Capability | FedRAMP 20x | FedRAMP Rev. 5 |
|---|---|---|
| Primary Model | Outcome- and KSI-based security validation | NIST SP 800-53 control-based assessment |
| Validation Approach | Persistent, automated, and evidence-driven validation | Traditional assessment testing and periodic validation |
| Core Compliance Object | Key Security Indicators (KSIs) | Security controls |
| Evidence Model | Automation-oriented and machine-readable evidence | Documents, narratives, and assessment artifacts |
| Authorization Documentation | 20x Certification Package and Security Decision Records | SSP, SAP, SAR, POA&M, and supporting artifacts |
| Ongoing Compliance | Ongoing Certification and persistent validation | Continuous Monitoring (ConMon) |
| Automation Emphasis | High — automation is central to validation and evidence management | Supported, but traditional documentation remains prominent |
| Continuum GRC Support | Supported — KSI management, automated evidence, persistent validation, remediation, and reporting | Supported — control mapping, SSP workflows, assessment evidence, POA&M, and ConMon |
Automate FedRAMP Key Security Indicators (KSIs)
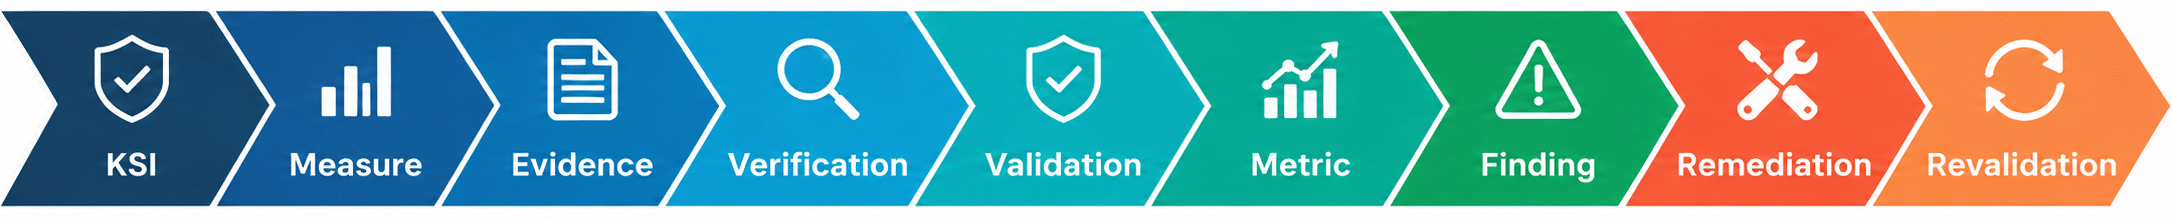
Key Security Indicators are at the center of the FedRAMP 20x model. Continuum GRC transforms KSIs into manageable compliance workflows by connecting each security outcome to responsible owners, measures, validation methods, evidence, metrics, findings, and remediation.
Manage the Complete KSI Lifecycle
With Continuum GRC, organizations can:
- Centralize applicable FedRAMP KSIs and requirements.
- Assign responsibility and accountability for each KSI.
- Define measures used to demonstrate security outcomes.
- Associate automated and manual validation methods with those measures.
- Collect and organize supporting technical evidence.
- Track persistent verification and validation activities.
- Maintain KSI metrics and historical results.
- Identify missing, outdated, failed, or insufficient evidence.
- Route exceptions and failures into remediation workflows.
- Track corrective actions through revalidation.
- Maintain evidence and validation history for independent assessment.
- Generate dashboards and reports showing current FedRAMP readiness and compliance status.
Instead of treating a KSI as a periodic compliance question, Continuum GRC makes it part of an ongoing operational workflow.
FedRAMP 20x vs. Rev. 5: Operational Differences
| FedRAMP 20x Area | Continuum GRC Support |
|---|---|
| Key Security Indicators (KSIs) | Centralize KSIs, measures, ownership, evidence, validation status, metrics, and remediation activities. |
| Automated Verification & Validation | Connect automated evidence collection and validation methods to applicable KSIs and security requirements. |
| Persistent Validation | Track validation results over time and identify security changes, failures, exceptions, and conditions requiring attention. |
| Security Decision Record (SDR) | Organize security decisions, implementation information, verification, validation, assessment results, and supporting artifacts. |
| Machine-Readable Information | Structure compliance information for automation, integration, repeatable processing, and JSON-based FedRAMP outputs where applicable. |
| Historical KSI Metrics | Preserve validation results and metrics over time to support historical reporting and applicable FedRAMP certification-class requirements. |
| Findings & Remediation | Convert failed validations and exceptions into tracked corrective actions, remediation workflows, and revalidation activities. |
| Independent Assessment Readiness | Organize evidence, measures, validation results, findings, and remediation history for independent verification and validation. |
| Ongoing Certification | Maintain current compliance data, evidence, validation results, vulnerabilities, changes, findings, and certification reporting. |
| Cross-Framework Mapping | Reuse applicable evidence and compliance information across FedRAMP, NIST, ISO, SOC 2, CMMC, and other mapped frameworks where appropriate. |
Automated FedRAMP Evidence Collection
FedRAMP 20x increases the importance of automation and current, measurable evidence. Continuum GRC helps replace repetitive evidence-gathering exercises with connected compliance workflows.
Evidence can be collected and exchanged through supported APIs, integrations, webhooks, automation workflows, file repositories, system-generated reports, and other data sources. Evidence is then associated with the applicable KSI, requirement, measure, validation activity, or assessment procedure.
From Technical Evidence to Compliance Status
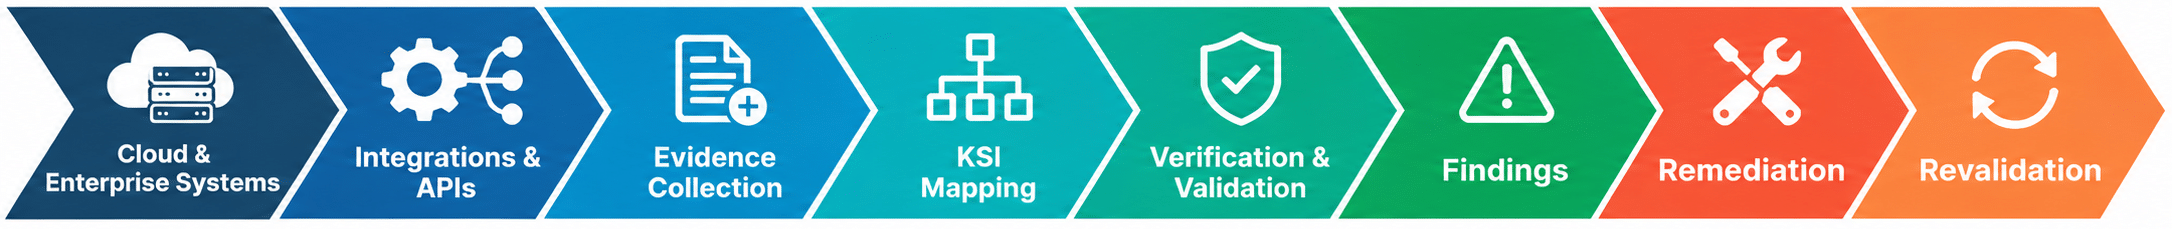
This approach helps compliance teams identify evidence that is missing, outdated, inconsistent, or requires attention before it becomes an assessment issue.
It also enables evidence collected for one requirement to be reused across mapped requirements and compliance frameworks when appropriate, reducing unnecessary duplicate evidence requests.
Human-Readable and Machine-Readable FedRAMP Compliance
FedRAMP 20x moves compliance information beyond static documents. Where FedRAMP provides a corresponding JSON schema, required machine-readable information must be supplied as valid JSON.
Continuum GRC helps organizations structure FedRAMP compliance information so requirements, evidence, measures, validation results, metrics, findings, and remediation data can be managed systematically rather than existing only in spreadsheets and narrative documents.
Structured compliance data supports automation, integrations, repeatable validation, reporting, evidence reuse, and preparation of required FedRAMP certification information.
The result is a compliance environment designed for both human review and machine-enabled security assurance.
Manage the FedRAMP Security Decision Record
Under the 2026 FedRAMP rules, the Security Decision Record (SDR) replaces the traditional SSP as the persistently maintained record of security decisions for applicable FedRAMP certification requirements.
Continuum GRC provides a centralized environment for organizing the information that supports the Security Decision Record, including:
- How applicable FedRAMP rules are implemented.
- Verification of security implementations.
- Validation that implementations are operating as intended.
- Independent verification and validation results.
- Responses and clarifications resulting from independent assessment.
- Rule-specific supporting artifacts.
- KSI measures and objectives.
- Persistent measurement cycles.
- KSI validation results and historical metrics.
- Version, update and source information.
Rather than recreating security documentation before each assessment, organizations can maintain the supporting compliance record as their environment, evidence and security decisions evolve.
20x Shift: The Security Decision Record replaces the traditional SSP for applicable FedRAMP 20x certification requirements and is maintained in both human-readable and machine-readable form.
AI-Assisted FedRAMP Compliance with AITAMBot™
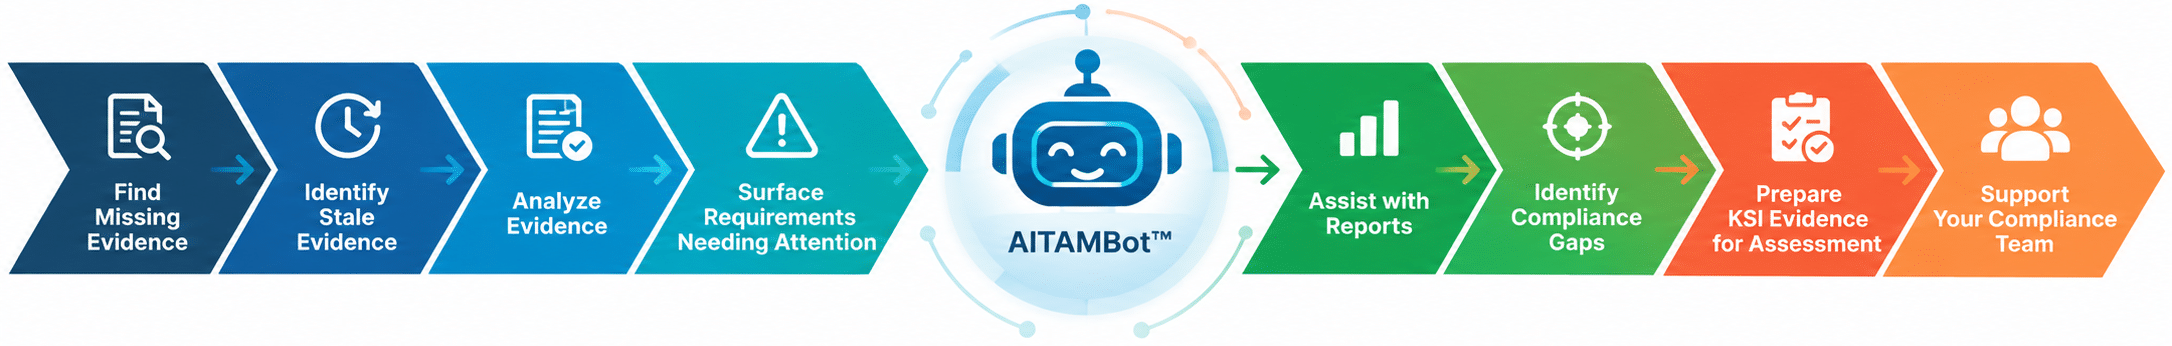
AITAMBot™ adds AI-assisted analysis to the FedRAMP compliance lifecycle, helping teams locate evidence, identify gaps, analyze compliance information, surface requirements needing attention, and prepare for validation and independent assessment.
AITAMBot can help compliance teams:
- Identify KSIs and requirements requiring attention.
- Locate supporting evidence across the compliance environment.
- Identify missing or potentially insufficient evidence.
- Surface failed or incomplete compliance activities.
- Analyze assessment and readiness information.
- Assist with compliance reporting.
- Identify remediation priorities.
- Query FedRAMP compliance information using natural language.
- Prepare teams for validation and assessment activities.
AITAMBot™ works alongside compliance professionals and assessors rather than replacing required independent judgment, verification, or validation.
Manage the FedRAMP 20x Certification Package
A FedRAMP 20x Certification Package is not simply a static collection of documents. It is maintained certification data that provides agencies and other authorized parties with a current view of the cloud service offering and the evidence supporting its FedRAMP Certification.
Continuum GRC helps organize and maintain the information supporting the major components of a 20x Certification Package:
Certification Package Overview
Maintain information describing the cloud service offering, assessment scope, information resources, information flows, third-party resources, policies and other required package information.
Security Decision Record
Maintain security decisions, implementation information, verification, validation, independent assessment information and supporting artifacts.
Key Security Indicators
Connect each applicable KSI to measures, evidence, validation methods, metrics, results and remediation.
Secure Configuration Guide
Organize information customers need to configure and operate the cloud service securely.
Ongoing Certification Data
Maintain current certification information, including required reports, vulnerability information, changes, incidents, availability information and other ongoing security data.
Continuum GRC brings these activities into a governed compliance lifecycle so certification information can remain current as the cloud service changes.
FedRAMP 20x Automation & Metrics Requirements
| Capability | Class A | Class B | Class C | Class D |
|---|---|---|---|---|
| Automated KSI Verification & Validation | May implement automated methods | Should have at least 1 automated method per KSI | Must have at least 2 automated methods per KSI | Must have at least 4 automated methods per KSI |
| Historical KSI Metrics | May provide historical metrics | Should provide historical metrics | Must provide at least 6 months of historical metrics | Must provide at least 18 months of historical metrics |
| Independent Assessment | Based on the underlying alternative security framework | All applicable KSIs assessed at least annually | All applicable KSIs assessed at least annually | All applicable KSIs assessed at least annually |
| Continuum GRC Support | Evidence & compliance management | Automation, KSI metrics & evidence management | Persistent validation & historical metrics | Advanced automation & extended historical assurance |
Persistent Validation & Ongoing Certification
FedRAMP compliance does not end when initial certification is achieved. The 20x model emphasizes maintaining current security information and demonstrating that security measures continue to operate as intended.
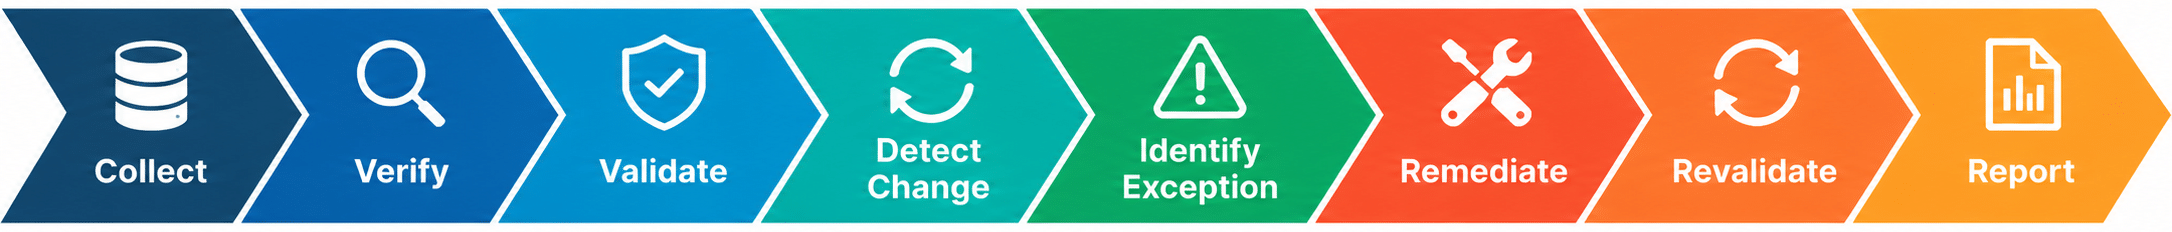
Continuum GRC supports this lifecycle by connecting ongoing evidence collection, KSI metrics, validation results, vulnerabilities, changes, findings, remediation activities and certification reporting.
Move From Point-in-Time Compliance to Continuous Assurance
| Area | FedRAMP 20x | FedRAMP Rev. 5 |
|---|---|---|
| Primary Security Model | Security outcomes, FedRAMP rules, and Key Security Indicators (KSIs) | NIST SP 800-53 Rev. 5 security controls and control baselines |
| Core Security Record | Security Decision Record (SDR), maintained as an ongoing security record | Traditional control implementation documentation, SSP-related content, and assessment artifacts |
| Key Security Indicators | Central to demonstrating measurable security outcomes | Not the primary assessment model |
| Verification & Validation | Persistent, measurable, and increasingly automated verification and validation | Traditional control assessment procedures and periodic testing |
| Automation Emphasis | High — automation is built into evidence, validation, metrics, and ongoing assurance | Supported, but the model remains more document- and control-assessment oriented |
| Machine-Readable Information | Strong emphasis on structured and JSON-based compliance information where required | Structured information is increasingly supported, but traditional documentation remains prominent |
| Evidence Model | Persistent evidence, measures, metrics, validation results, and historical assurance data | Control assessment evidence, narratives, test results, and authorization artifacts |
| Ongoing Security Assurance | Ongoing Certification with persistent validation and current security data | Traditional Continuous Monitoring (ConMon) |
| Independent Assessment | Independent verification and validation based on applicable certification class and FedRAMP rules | Independent assessment against applicable NIST SP 800-53 and FedRAMP requirements |
| Findings & Remediation | Findings feed directly into remediation and revalidation workflows | Findings are managed through assessment results, POA&M, and remediation activities |
| Continuum GRC Support | KSI management, automated evidence, persistent validation, SDR support, historical metrics, remediation, and Ongoing Certification | Control mapping, SSP-related workflows, assessment evidence, POA&M, remediation, and ConMon |
FedRAMP Rev. 5 Authorization, Assessment & ConMon Automation
Continuum GRC continues to support organizations operating under traditional FedRAMP Rev. 5 requirements, including authorization documentation, security control implementation, assessment preparation, POA&M management, remediation, and Continuous Monitoring.
The platform provides preconfigured modules supporting CSP and independent assessment workflows, including:
CSP Module Bundle includes:
- System Security Plan (SSP)
- Plan of Action and Milestones (POA&M)
- Customer Responsibility Matrix
- Electronic Authentication (E-Authentication) Plan
- Privacy Impact Assessment (PIA)
- Rules of Behavior (RoB)
- Information System Contingency Plan (ISCP)
- CIS
- Federal Information Processing Standard (FIPS) 199 Categorization
- Integrated Inventory Workbook
- Information System Security Policies and Procedures
- Configuration Management (CM) Plan
- Control Implementation Summary (CIS)
- CIS Worksheet
- IT Contingency Plan (CP)
- Incident Response Plan (IRP)
- Rules of Behavior (ROB)
- AC Access Control
- AT Awareness and Training
- AU Audit and Accountability
- CA Certification, Accreditation, and Security Assessment
- CM Configuration Management
- CP Contingency Planning
- IA Identification and Authentication
- IR Incident Response
- MA Maintenance
- MP Media Protection
- PE Physical and Environmental Protection
- PL Planning
- PS Personnel Security
- RA Risk Assessment
- SA System and Services Acquisition
- SC System and Communications Protection
- SI System and Information Integrity
- PM Project Management
3PAO Module Bundle includes:
- Security Assessment Report (SAR)
- Security Assessment Plan (SAP)
- SAR Appendix A FedRAMP Risk Exposure Table (RET)
- SAR Appendix B Moderate Security Requirements Traceability Matrix
- Annual Assessment Controls Selection Worksheet
FedRAMP+ DoD IL
- FedRAMP+ System Security Plan Information Impact Level 2 (Non-Controlled Unclassified Information)
- FedRAMP+ System Security Plan Information Impact Level 4 (Controlled Unclassified Information)
- FedRAMP+ System Security Plan Information Impact Level 5 (Controlled Unclassified Information)
- FedRAMP+ System Security Plan Information Impact Level 6 (Controlled Unclassified Information)
ConMon
- Continuous Monitoring Activities & Deliverables: Continuous
- Continuous Monitoring Activities & Deliverables: Weekly
- Continuous Monitoring Activities & Deliverables: 10 days
- Continuous Monitoring Activities & Deliverables: Monthly
- Continuous Monitoring Activities & Deliverables: 60 days
- Continuous Monitoring Activities & Deliverables: Quarterly (90 days)
- Continuous Monitoring Activities & Deliverables: Annual
- Continuous Monitoring Activities & Deliverables: Every 2 years
- Continuous Monitoring Activities & Deliverables: Every 3 years
- Continuous Monitoring Activities & Deliverables: Every 5 years
- FedRAMP Significant Change Request Form
- FedRAMP Significant Change Request Form: Attachment A
One Platform for the FedRAMP Compliance Lifecycle
FedRAMP compliance involves much more than completing an assessment. Cloud service providers must maintain security requirements, evidence, vulnerabilities, changes, findings, remediation activities, validation results and certification information throughout the lifecycle of the service.
Continuum GRC connects these activities within one compliance environment.
Prepare — Identify applicable requirements, gaps, owners and evidence.
Automate — Connect systems and workflows to collect and maintain compliance evidence.
Validate — Track verification, validation, KSI measures and compliance results.
Remediate — Convert findings and exceptions into accountable corrective actions.
Assess — Organize evidence and results for independent assessment.
Maintain — Support persistent validation, historical metrics, Continuous Monitoring or Ongoing Certification.
The result is a traceable compliance lifecycle from initial readiness through independent assessment and ongoing security assurance.
Reduce Manual FedRAMP Compliance Work
FedRAMP becomes expensive and difficult to maintain when requirements, evidence, technical teams, assessors, findings and remediation activities are managed through disconnected spreadsheets, email and document repositories.
Continuum GRC centralizes these activities and automates repeatable work.
Evidence can be mapped to applicable requirements, reused where appropriate, assigned to responsible owners, evaluated for readiness, and maintained throughout the compliance lifecycle. Findings flow into remediation workflows, and updated evidence can be connected to revalidation activities.
For organizations managing multiple compliance obligations, Continuum GRC can also map applicable evidence across FedRAMP, NIST and other supported frameworks—helping reduce duplicate evidence collection and repetitive compliance work.
Collect evidence once. Map it intelligently. Reuse it where appropriate.
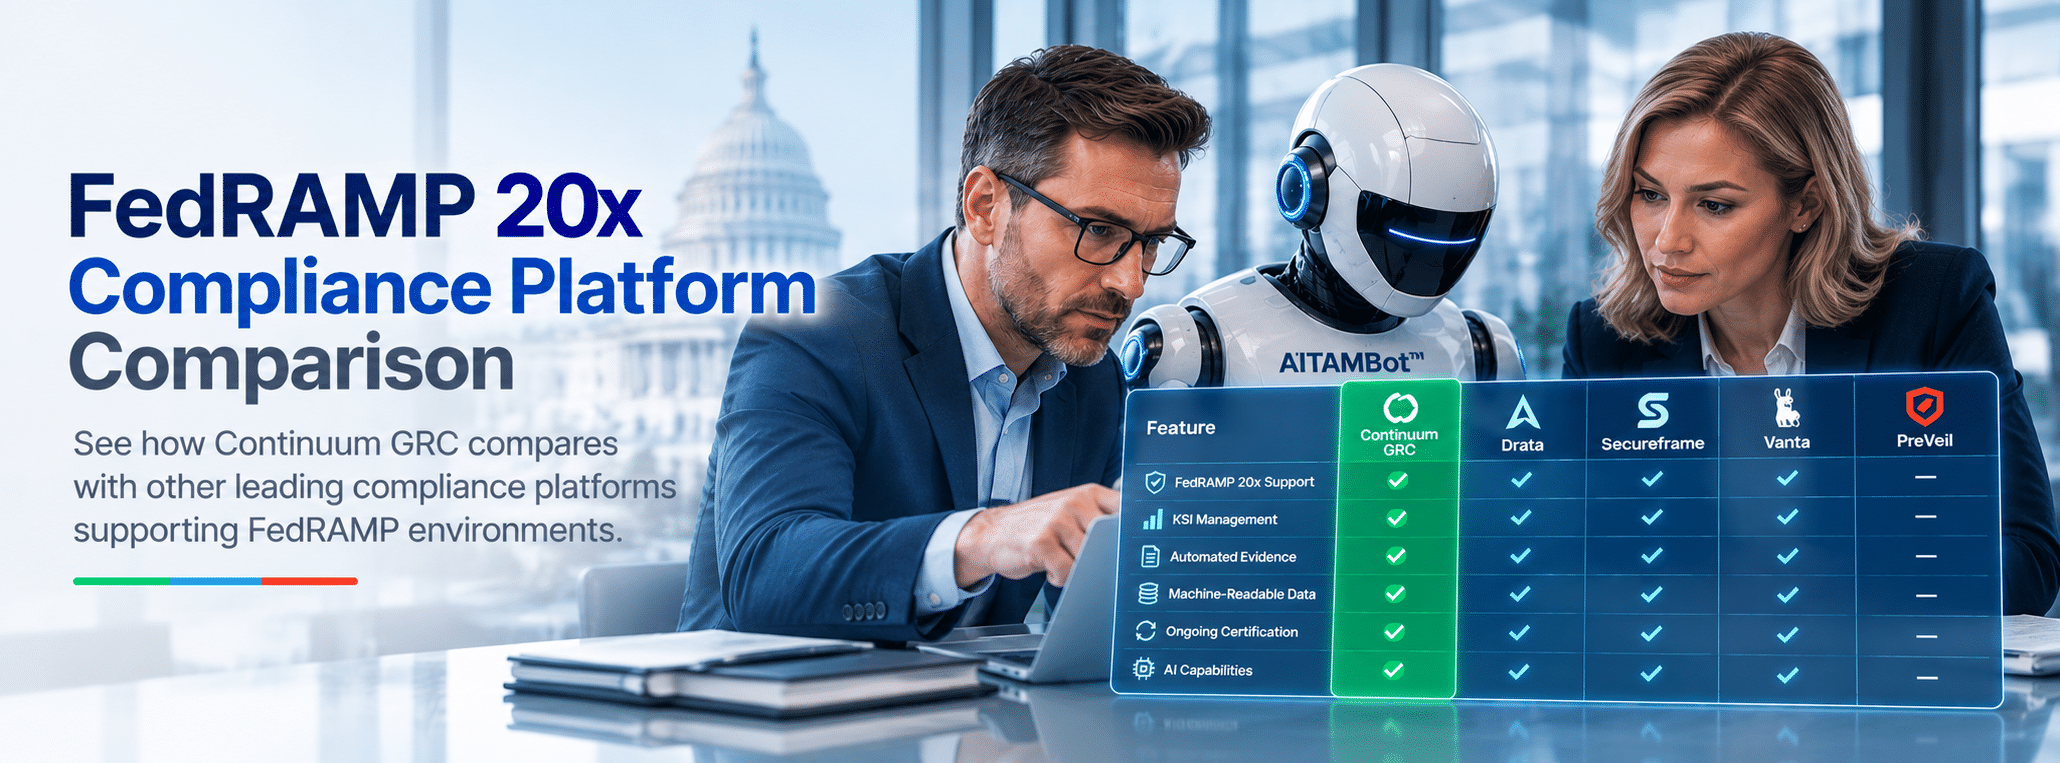
FedRAMP 20x Compliance Platform Comparison – 2026
Compare how leading compliance platforms support FedRAMP 20x automation, Key Security Indicators (KSIs), evidence collection, machine-readable compliance, ongoing certification, and traditional FedRAMP Rev. 5 workflows.
| Feature | Continuum GRC | Drata | Secureframe | Vanta | PreVeil |
|---|---|---|---|---|---|
| FedRAMP 20x Support | ✅ | Available / evolving | ✅ | ✅ | Not positioned as a FedRAMP 20x GRC platform |
| Key Security Indicator (KSI) Management | ✅ Centralized KSI workflow | Public 20x guidance available | ✅ KSI framework mapped to controls and tests | ✅ KSI readiness and gap tracking | — |
| KSI Evidence Mapping | ✅ | Verify current product capability | ✅ | ✅ | — |
| Automated Evidence Collection | ✅ | ✅ | ✅ | ✅ | Limited / not primary use case |
| Persistent Verification & Validation Workflows | ✅ | Not confirmed from public documentation | ✅ Continuous monitoring and automated tests | ✅ Automated continuous control testing | — |
| Machine-Readable FedRAMP Data | ✅ Structured compliance data / JSON support | Not confirmed from public documentation | ✅ Machine-readable 20x outputs demonstrated | ✅ Machine-readable outputs | — |
| Security Decision Record (SDR) Management | ✅ | Not confirmed from public documentation | Not confirmed from public documentation | Not confirmed from public documentation | — |
| Historical KSI Metrics | ✅ | Not confirmed from public documentation | Not confirmed from public documentation | Not confirmed from public documentation | — |
| Findings → Remediation → Revalidation Workflow | ✅ | ✅ General remediation workflows | ✅ General remediation workflows | ✅ General remediation workflows | — |
| Ongoing Certification Support | ✅ | Not confirmed from public documentation | ✅ 20x continuous monitoring support | ✅ Ongoing monitoring / continuous validation | — |
| AI-Assisted Evidence Analysis | ✅ AITAMBot™ | ✅ Drata AI | ✅ AI Evidence Validation | ✅ Vanta AI capabilities | — |
| Dedicated AI Auditor | ✅ AITAMBot™ | Not positioned as a dedicated AI auditor | Not positioned as a dedicated AI auditor | Not positioned as a dedicated AI auditor | — |
| FedRAMP Rev. 5 Support | ✅ | ✅ | ✅ | ✅ | Not a full FedRAMP GRC platform |
| POA&M Management & Remediation Tracking | ✅ | ✅ | ✅ | ✅ | — |
| NIST SP 800-53 / FedRAMP Mapping | ✅ | ✅ | ✅ | ✅ | Limited to applicable security use cases |
| Cross-Framework Evidence Reuse | ✅ 100+ mapped frameworks | ✅ | ✅ | ✅ | Limited |
| Ability to Create Custom Frameworks | ✅ | ✅ | ✅ | ✅ | — |
| Integrated Independent Assessment Option | ✅ Available through independent accredited assessment services | Partner ecosystem | Partner ecosystem | Partner ecosystem | Partner ecosystem |
| Real-Time Compliance Dashboard | ✅ | ✅ | ✅ | ✅ | Limited |
| Free Trial / Readiness Tools | ✅ Free Tools & FedRAMP Resources | Varies | Varies | Varies | Varies |
Comparison note: Public product capabilities change frequently. Competitor information shown here should be periodically reviewed against current vendor documentation. “Not confirmed from public documentation” indicates that a comparable FedRAMP 20x-specific capability was not confirmed from current public product materials at the time of review.
Frequently Asked Questions
What is FedRAMP 20x?
FedRAMP 20x is FedRAMP's modernized certification model emphasizing measurable security outcomes, Key Security Indicators, automation, persistent verification and validation, machine-readable information, and continuously maintained certification data.
What are FedRAMP Key Security Indicators?
KSIs describe important security outcomes that a cloud service provider must demonstrate. Providers maintain measures, evidence, verification, validation and, depending on Certification Class, historical metrics and automated validation methods supporting applicable KSIs.
How does Continuum GRC automate FedRAMP KSIs?
Continuum GRC connects KSIs to owners, measures, evidence, validation methods, metrics, findings and remediation workflows. This allows organizations to manage KSI compliance as an ongoing process rather than a periodic evidence-gathering exercise.
Does FedRAMP 20x require automated KSI validation?
Automation requirements depend on Certification Class. Under the 2026 rules, Class B providers should implement at least one automated method per KSI; Class C providers must implement at least two; and Class D providers must implement at least four.
What is the FedRAMP Security Decision Record?
The Security Decision Record is the maintained record of how applicable FedRAMP rules are implemented, verified and validated. FedRAMP requires it in human-readable and JSON formats and includes independent verification and validation information and applicable supporting artifacts.
Does FedRAMP 20x still require independent assessment?
Yes. For Classes B, C and D, applicable KSIs must be included in a FedRAMP independent assessment at least annually. Class A follows the independent verification and validation expectations of its underlying alternative security framework.
Does Continuum GRC support both FedRAMP 20x and Rev. 5?
Yes. Continuum GRC can support modern FedRAMP 20x workflows as well as traditional Rev. 5 control, evidence, assessment, POA&M and Continuous Monitoring activities.
Does Continuum GRC replace a 3PAO?
No. Continuum GRC does not replace a required independent 3PAO assessment. AITAMBot™ automates and assists many of the evidence analysis, compliance review, gap identification, validation-support, and reporting activities performed during assessment preparation and ongoing compliance. When FedRAMP requires independent verification and validation, that function remains with the required independent assessor.
Contact us using the form below or calling us at 1-888-896-6207 for assistance.
About FedRAMP in 2026
The Federal Risk and Authorization Management Program (FedRAMP) establishes standardized security requirements and processes for cloud services used by the U.S. federal government.
FedRAMP now supports both modernized 20x certification approaches and Rev. 5 requirements under the FedRAMP Consolidated Rules for 2026.
FedRAMP 20x
FedRAMP 20x emphasizes measurable security outcomes, Key Security Indicators, persistent verification and validation, automation, machine-readable certification information, independent assessment, and Ongoing Certification.
The model is designed to make security information more current, reusable and technically verifiable throughout the lifecycle of a cloud service.
FedRAMP Rev. 5
FedRAMP Rev. 5 continues to use NIST SP 800-53 Revision 5 security controls and traditional control-based assessment processes while transitioning to applicable requirements established by the Consolidated Rules for 2026.
Independent Assessment
FedRAMP requires independent verification and validation according to the applicable certification type, class and rules. Continuum GRC helps cloud service providers organize the requirements, evidence, validation results, findings and remediation history needed to prepare for these assessments.
Ongoing Security Assurance
Achieving FedRAMP Certification is not the end of the compliance lifecycle. Cloud service providers must continue maintaining required security information, responding to vulnerabilities and changes, performing required validation activities, addressing findings, and supplying required ongoing certification information.
Continuum GRC provides a centralized platform for managing that lifecycle from readiness through assessment and ongoing assurance.