CMMC Compliance Automation & Level 2 Assessment Readiness
Table of Contents
TogglePrepare for CMMC assessments with automated NIST SP 800-171 control management, evidence collection, System Security Plans, POA&M tracking, and AI-assisted readiness workflows.
Continuum GRC helps defense contractors and subcontractors manage CMMC cybersecurity requirements in one centralized compliance platform.
Connect applicable CMMC practices with control implementation records, supporting evidence, assessment preparation, remediation, and continuous monitoring—without managing disconnected spreadsheets, documents, and compliance tools.
Build a more efficient path from CMMC readiness to ongoing compliance management.
CMMC Level 2 readiness capabilities include:
- Map the 110 security requirements to implementation statements and supporting evidence.
- Assign control owners and track implementation status.
- Organize evidence against applicable assessment objectives.
- Maintain System Security Plans and supporting security documentation.
- Track assessment scope and associated assets.
- Identify missing evidence and potential control gaps.
- Manage findings, corrective actions, and POA&Ms.
- Coordinate assessment requests and readiness reporting.
Continuum GRC supports both Level 2 self-assessment preparation and independent C3PAO assessment readiness, as applicable. Official certification assessments remain separate from the software platform.
Built for Defense Contractors Preparing for CMMC
Organizations supporting the Department of Defense must understand which CMMC requirements apply to their contracts, systems, and information environments.
Continuum GRC helps defense contractors, subcontractors, managed service providers, and compliance teams organize their cybersecurity activities across applicable CMMC assessment levels.
The platform helps organizations:
- Map CMMC requirements to security controls and responsible personnel.
- Maintain implementation documentation and supporting evidence.
- Prepare for CMMC Level 2 self-assessments or C3PAO assessments, as applicable.
- Identify gaps and manage corrective actions.
- Maintain System Security Plans and POA&Ms.
- Track assessment readiness and recurring compliance obligations.
- Reuse relevant evidence across CMMC, DFARS, and NIST SP 800-171.
Continuum GRC supports CMMC readiness and compliance management. CMMC assessment results and certification status are determined through the applicable authorized assessment processes.
What Is CMMC and Why Does It Matter?
The Cybersecurity Maturity Model Certification (CMMC) program establishes cybersecurity assessment requirements for Department of Defense contractors and subcontractors handling Federal Contract Information (FCI) or Controlled Unclassified Information (CUI).
CMMC requirements are incorporated into applicable defense contracts through DFARS 252.204-7021. Depending on the required level, organizations may complete a self-assessment, undergo an assessment by an authorized CMMC Third-Party Assessment Organization (C3PAO), or undergo a government-led assessment.
Continuum GRC helps organizations manage the operational work behind these requirements, including security control implementation, evidence collection, assessment documentation, findings, remediation, and ongoing monitoring.
CMMC readiness is not a one-time documentation exercise. Maintaining accurate security records, addressing deficiencies, and monitoring system changes are essential to sustaining the required CMMC status.
Understanding the Three CMMC Levels
| CMMC Level | Security Requirements | Assessment Pathway | Continuum GRC Support |
|---|---|---|---|
|
Level 1 Foundational |
15 safeguarding requirements derived from FAR 52.204-21, focused on protecting Federal Contract Information (FCI). | Annual organizational self-assessment and annual affirmation of compliance. | Control mapping, implementation tracking, evidence management, self-assessment documentation, and recurring monitoring. |
|
Level 2 Advanced |
110 security requirements aligned with NIST SP 800-171 Revision 2, focused on protecting Controlled Unclassified Information (CUI). | Triennial self-assessment or assessment by an authorized CMMC Third-Party Assessment Organization (C3PAO), as required by the contract. Annual affirmations also apply. | Assessment readiness, System Security Plans (SSPs), POA&M tracking, automated evidence collection, remediation workflows, and AI-assisted compliance analysis. |
|
Level 3 Expert |
Level 2 requirements plus 24 selected enhanced security requirements derived from NIST SP 800-172, addressing advanced cybersecurity threats. | Government-led assessment following the required Level 2 certification prerequisite. Triennial assessment cycle and annual affirmations apply. | Enhanced control mapping, advanced security documentation, assessment evidence management, corrective-action tracking, and continuous monitoring. |
Important: The required CMMC level and assessment pathway are determined by the applicable DoD solicitation or contract. Continuum GRC supports compliance management and assessment readiness but does not independently issue CMMC certifications or government assessment determinations.
Continuum GRC includes dedicated CMMC Level 1, Level 2, and Level 3 compliance modules. Organizations can manage applicable requirements, document control implementation, assign responsibilities, organize evidence, and track assessment readiness within a unified GRC environment.
For Level 2 assessments, the platform supports the 110 security requirements associated with the CMMC Level 2 assessment baseline. The CMMC program's applicable NIST SP 800-171 revision should be distinguished from later revisions used in other cybersecurity initiatives.
CMMC Level 2 Assessment Readiness & Evidence Management
Preparing for a CMMC Level 2 assessment requires more than implementing security technologies. Organizations must demonstrate that applicable security requirements are satisfied within the defined assessment scope and support those determinations with appropriate evidence.
Continuum GRC helps compliance teams organize the information needed to prepare for an assessment.
CMMC Level 2 readiness capabilities include:
- Mapping the 110 security requirements to assigned control owners.
- Maintaining implementation statements and supporting documentation.
- Organizing policies, procedures, system records, and technical evidence.
- Tracking assessment objectives and readiness gaps.
- Maintaining System Security Plans and assessment scope documentation.
- Recording findings and corrective actions.
- Managing POA&M activities where permitted by CMMC rules.
- Monitoring changes that may affect readiness or CMMC status.
Centralized evidence and control management help reduce fragmented documentation and provide assessment teams with a more consistent record of implementation.
Continuum GRC supports preparation for authorized CMMC assessments. Assessment determinations remain the responsibility of the applicable assessment organization or government authority.
Automated CMMC Evidence Collection & Control Validation Support
CMMC assessment preparation often involves collecting security documentation from identity management systems, cloud platforms, endpoint tools, vulnerability scanners, ticketing systems, and document repositories.
Continuum GRC helps organizations centralize and organize evidence through supported integrations, APIs, webhooks, and configurable compliance workflows.
Evidence can be associated with applicable security requirements, implementation statements, assessment activities, and corrective actions.
From CMMC Requirements to Continuous Readiness
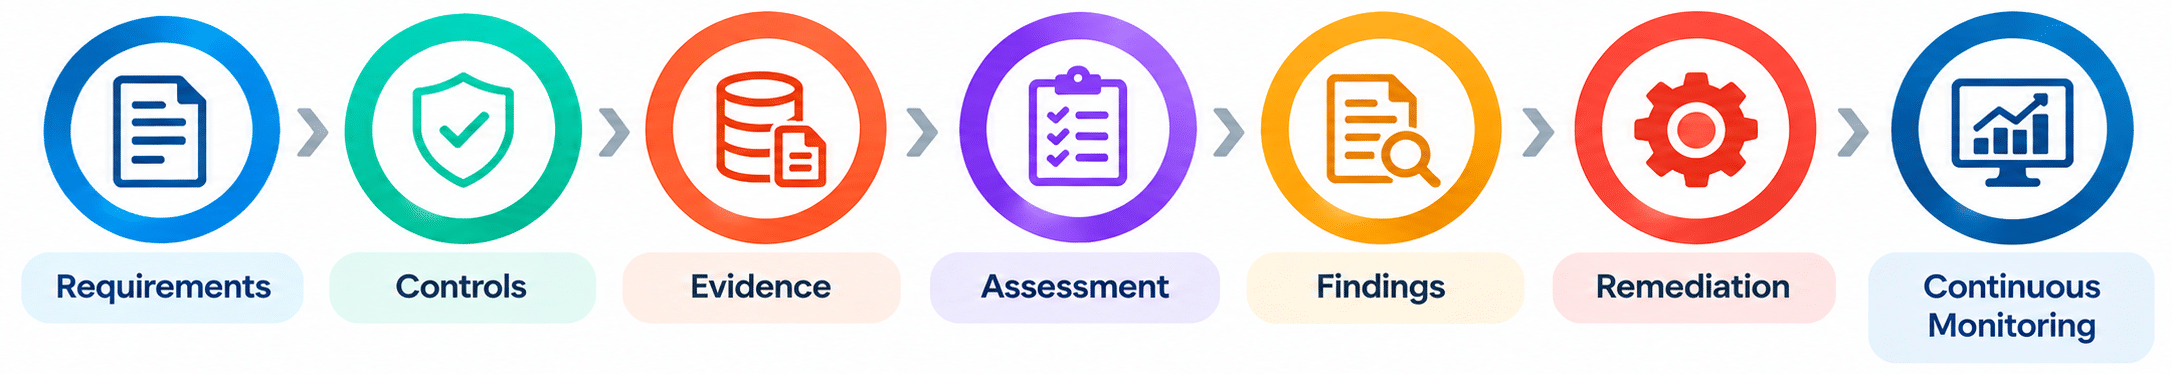
By connecting these activities, Continuum GRC helps organizations identify missing evidence, reduce repeated documentation requests, and maintain visibility into assessment preparation.
Automated evidence collection supports assessment activities but does not, by itself, establish that a CMMC security requirement has been satisfied.
CMMC System Security Plans, POA&Ms & Remediation Management
Continuum GRC provides structured workflows for maintaining CMMC assessment documentation and tracking security deficiencies.
System Security Plans (SSPs)
Maintain information describing system boundaries, operating environments, security requirements, implementation details, responsible personnel, and supporting evidence.
Plans of Action and Milestones (POA&Ms)
Record eligible deficiencies, assign corrective actions, establish remediation milestones, track supporting evidence, and monitor closure activities.
Assessment Findings
Organize identified gaps, implementation weaknesses, evidence deficiencies, and related corrective actions to support readiness reviews.
Remediation Tracking
Maintain visibility into assigned tasks, responsible personnel, deadlines, remediation status, and follow-up activities.
CMMC places specific restrictions on which requirements may be addressed through a POA&M and how quickly eligible items must be closed. Maintaining a POA&M does not automatically establish an acceptable CMMC status.
Current CMMC Implementation Status — October 2026
CMMC requirements are being incorporated into Department of Defense solicitations and contracts through a phased implementation process.
Defense contractors should review current solicitations, contract clauses, required CMMC levels, and assessment pathways rather than assuming that every contract requires the same certification.
Organizations preparing for CMMC Level 2 should establish assessment boundaries, document applicable NIST SP 800-171 security requirements, maintain supporting evidence, and address readiness deficiencies before the required assessment.
Continuum GRC helps defense contractors prepare for these obligations and maintain compliance records as contract requirements and system environments change.
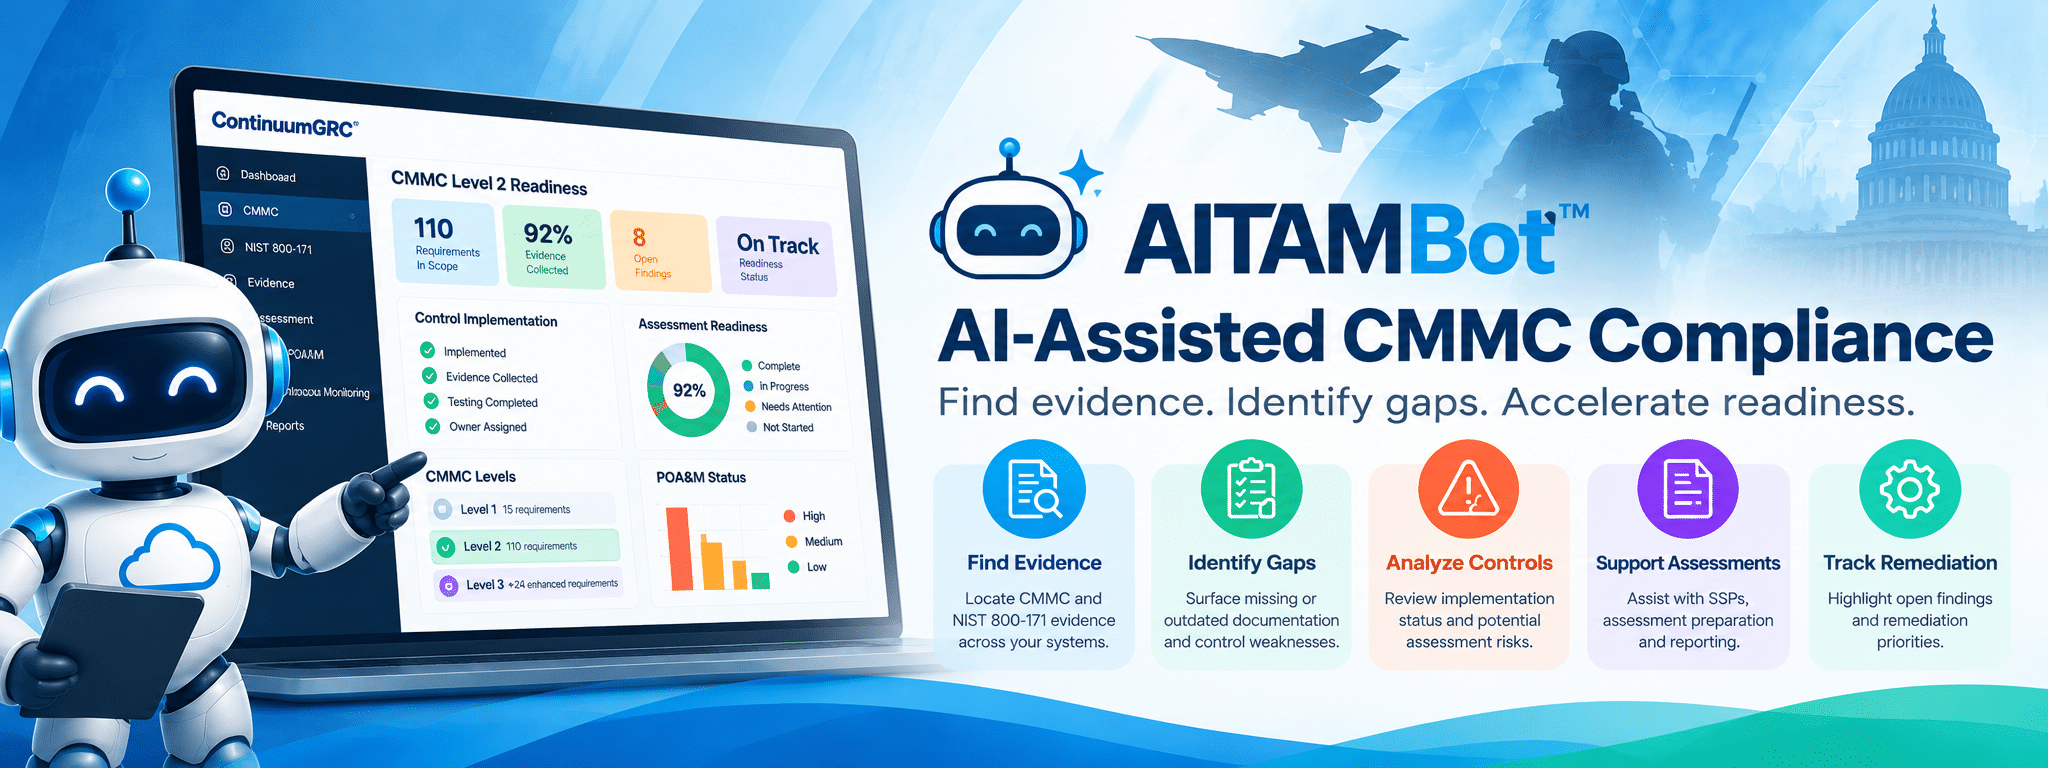
AI-Assisted CMMC Compliance with AITAMBot™
AITAMBot™ helps defense contractors accelerate CMMC readiness by analyzing available compliance records, identifying potential documentation gaps, and surfacing security requirements that need attention.
AI-assisted CMMC capabilities include:
- Locating evidence associated with CMMC requirements.
- Identifying missing or outdated policies and procedures.
- Reviewing control implementation documentation.
- Highlighting potential readiness gaps.
- Summarizing open findings and remediation priorities.
- Supporting SSP and assessment documentation preparation.
- Answering natural-language questions about compliance records.
- Helping teams prepare for recurring compliance reviews.
AITAMBot™ provides intelligent assistance within the Continuum GRC platform. It does not independently determine CMMC certification status or replace authorized C3PAO or government assessments.
Reuse Evidence Across CMMC, DFARS & NIST SP 800-171
Defense contractors frequently manage overlapping cybersecurity obligations under CMMC, DFARS, and NIST SP 800-171.
Continuum GRC helps organizations map shared security requirements and associate relevant documentation with multiple compliance workflows.
Organizations can reduce repetitive evidence collection while maintaining separate records for contractual requirements, SPRS assessment information, and CMMC assessment status.
Shared evidence does not make the programs interchangeable. A current SPRS assessment score does not automatically satisfy a contractual requirement for CMMC certification, and CMMC certification does not eliminate other applicable DFARS obligations.
CMMC Level 2 Compliance & Assessment Readiness Platform Comparison – 2026
Compare CMMC compliance automation platforms based on NIST SP 800-171 control management, assessment readiness, evidence collection, SSPs, POA&Ms, AI-assisted compliance, and continuous monitoring.
| Feature | Continuum GRC | Drata | Secureframe | Vanta | PreVeil |
|---|---|---|---|---|---|
| Platform & Framework Capabilities | |||||
| FedRAMP Authorized SaaS Platform | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| CMMC Level 1, Level 2 & Level 3 Modules | ✓ Yes | Verify level coverage | Verify level coverage | Verify level coverage | Verify level coverage |
| NIST SP 800-171 Control Mapping | ✓ Yes | Supported | Supported | Supported | Supported |
| NIST SP 800-172 Enhanced Requirements | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| Custom Compliance Framework Creation | ✓ Yes | Supported | Supported | Supported | Not publicly confirmed |
| Compliance Framework Library | 100+ Frameworks | Multiple Frameworks | Multiple Frameworks | Multiple Frameworks | CMMC / NIST Focus |
| CMMC Assessment Readiness & Documentation | |||||
| CMMC Level 2 Assessment Readiness | ✓ Yes | Supported | Supported | Supported | Supported |
| CMMC Scoping & Asset Documentation | ✓ Configurable | Verify scope features | Verify scope features | Verify scope features | Verify scope features |
| System Security Plan (SSP) Management | ✓ Yes | Verify current offering | Supported | Verify current offering | Supported |
| POA&M Management & Remediation Tracking | ✓ Yes | Supported | Supported | Supported | Supported |
| Assessment Evidence Organization | ✓ Yes | Supported | Supported | Supported | Supported |
| Independent C3PAO Assessment Services | Available separately through Lazarus Alliance | Verify partner options | Verify partner options | Verify partner options | Verify partner options |
| Evidence Automation & Continuous Monitoring | |||||
| Automated Evidence Collection | ✓ Yes | Supported | Supported | Supported | Supported |
| Cross-Framework Evidence Reuse | ✓ Yes | Supported | Supported | Supported | Verify current offering |
| Continuous Monitoring & Alerts | ✓ Yes | Supported | Supported | Supported | Verify current offering |
| Control Implementation Tracking | ✓ Yes | Supported | Supported | Supported | Supported |
| Real-Time Compliance Dashboards | ✓ Yes | Supported | Supported | Supported | Supported |
| AI-Assisted Compliance & Readiness Tools | |||||
| AI-Assisted Compliance Analysis | ✓ AITAMBot™ | Drata AI | Secureframe AI | Vanta AI | Verify current offering |
| Dedicated AI Auditor Tool | ✓ AITAMBot™ | Not directly comparable | Not directly comparable | Not directly comparable | Not publicly confirmed |
| Built-In CMMC Templates & Policies | ✓ Yes | Supported | Supported | Supported | Supported |
| Free 14-Day Trial (No Credit Card) | ✓ Yes | Verify current terms | Verify current terms | Verify current terms | Verify current terms |
| Free CMMC Readiness Tools | ✓ Free CMMC Compliance Tools | Verify current offering | Verify current offering | Verify current offering | Verify current offering |
Comparison notes: Feature availability may vary by subscription, configuration, service scope, and product updates. "Not publicly confirmed" indicates that the specific capability has not been verified for this comparison and does not mean the vendor lacks the capability. Continuum GRC provides compliance management and assessment readiness software. Independent CMMC certification assessments are separate services performed through authorized assessment organizations. AITAMBot™ supports compliance professionals but does not replace authorized CMMC assessors.
CMMC Assessment, Documentation & Continuous Monitoring Modules
Continuum GRC provides dedicated CMMC Level 1, Level 2, and Level 3 compliance modules supported by integrated control management, assessment documentation, evidence collection, POA&M tracking, and continuous monitoring.
These capabilities operate within Continuum GRC's broader library of 100+ compliance frameworks, allowing organizations to manage applicable cybersecurity requirements across multiple programs without maintaining entirely separate compliance records.
Modules include:
- Cybersecurity Maturity Model Certification (CMMC) Level 1
- Cybersecurity Maturity Model Certification (CMMC) Level 2
- Cybersecurity Maturity Model Certification (CMMC) Level 3
- C3PAO Assessment Level 1
- C3PAO Assessment Level 2
- C3PAO Assessment Level 3
FAQ
What is CMMC?
The Cybersecurity Maturity Model Certification (CMMC) is a Department of Defense program establishing cybersecurity assessment requirements for contractors and subcontractors handling Federal Contract Information or Controlled Unclassified Information.
Who needs CMMC certification?
Organizations must meet the CMMC level and assessment requirements specified in applicable DoD solicitations and contracts. Not every organization or contract requires third-party certification.
What is CMMC Level 2?
CMMC Level 2 addresses 110 security requirements aligned with the program's applicable NIST SP 800-171 baseline. Depending on the contract, an organization may require a self-assessment or an authorized C3PAO assessment.
Does CMMC Level 2 require a C3PAO assessment?
Not always. Some Level 2 requirements permit self-assessment, while others require an authorized C3PAO assessment. The applicable contract determines the required pathway.
How many requirements are in CMMC Level 2?
CMMC Level 2 includes 110 security requirements. Assessment activities evaluate the applicable requirements and their associated assessment objectives.
What is a CMMC System Security Plan?
An SSP describes the assessed system, its security boundary, operating environment, and implementation of applicable security requirements.
Can a CMMC assessment include POA&Ms?
Certain CMMC assessment deficiencies may qualify for conditional status and POA&M remediation. Strict eligibility, scoring, and closure requirements apply. Not every security deficiency may be placed on a POA&M.
How long does a CMMC Level 2 assessment take?
The timeline varies with the assessment boundary, organizational complexity, documentation quality, evidence availability, and number of findings. Readiness activities and the formal assessment should be treated as separate phases.
What is the difference between CMMC and DFARS?
DFARS contains contractual cybersecurity obligations. CMMC establishes assessment and status requirements incorporated into applicable defense contracts. The two programs overlap but are not interchangeable.
Does an SPRS score replace CMMC certification?
No. SPRS assessment information does not replace a required CMMC assessment or certification status.
Can CMMC evidence be reused across other frameworks?
Yes, when the evidence is relevant to the same requirements, systems, and assessment period. Continuum GRC supports mapping and reuse across applicable compliance frameworks.
Does Continuum GRC provide CMMC certification?
Continuum GRC provides compliance management and assessment readiness software. Required certification assessments are performed through the applicable authorized assessment process.
How does AITAMBot™ help with CMMC readiness?
AITAMBot™ assists with evidence discovery, documentation analysis, identifying potential gaps, and tracking readiness activities. It does not replace authorized assessors.
How often must CMMC status be renewed?
Level 1 self-assessments are annual. Final Level 2 status generally follows a three-year assessment cycle with annual affirmations. Other assessment and conditional-status rules may apply.
Does Continuum GRC support CMMC Level 3?
Yes. Continuum GRC includes a CMMC Level 3 compliance module for organizing applicable enhanced security requirements, documentation, evidence, and assessment readiness.
Contact us using the form below or calling us at 1-888-896-6207 for assistance.