


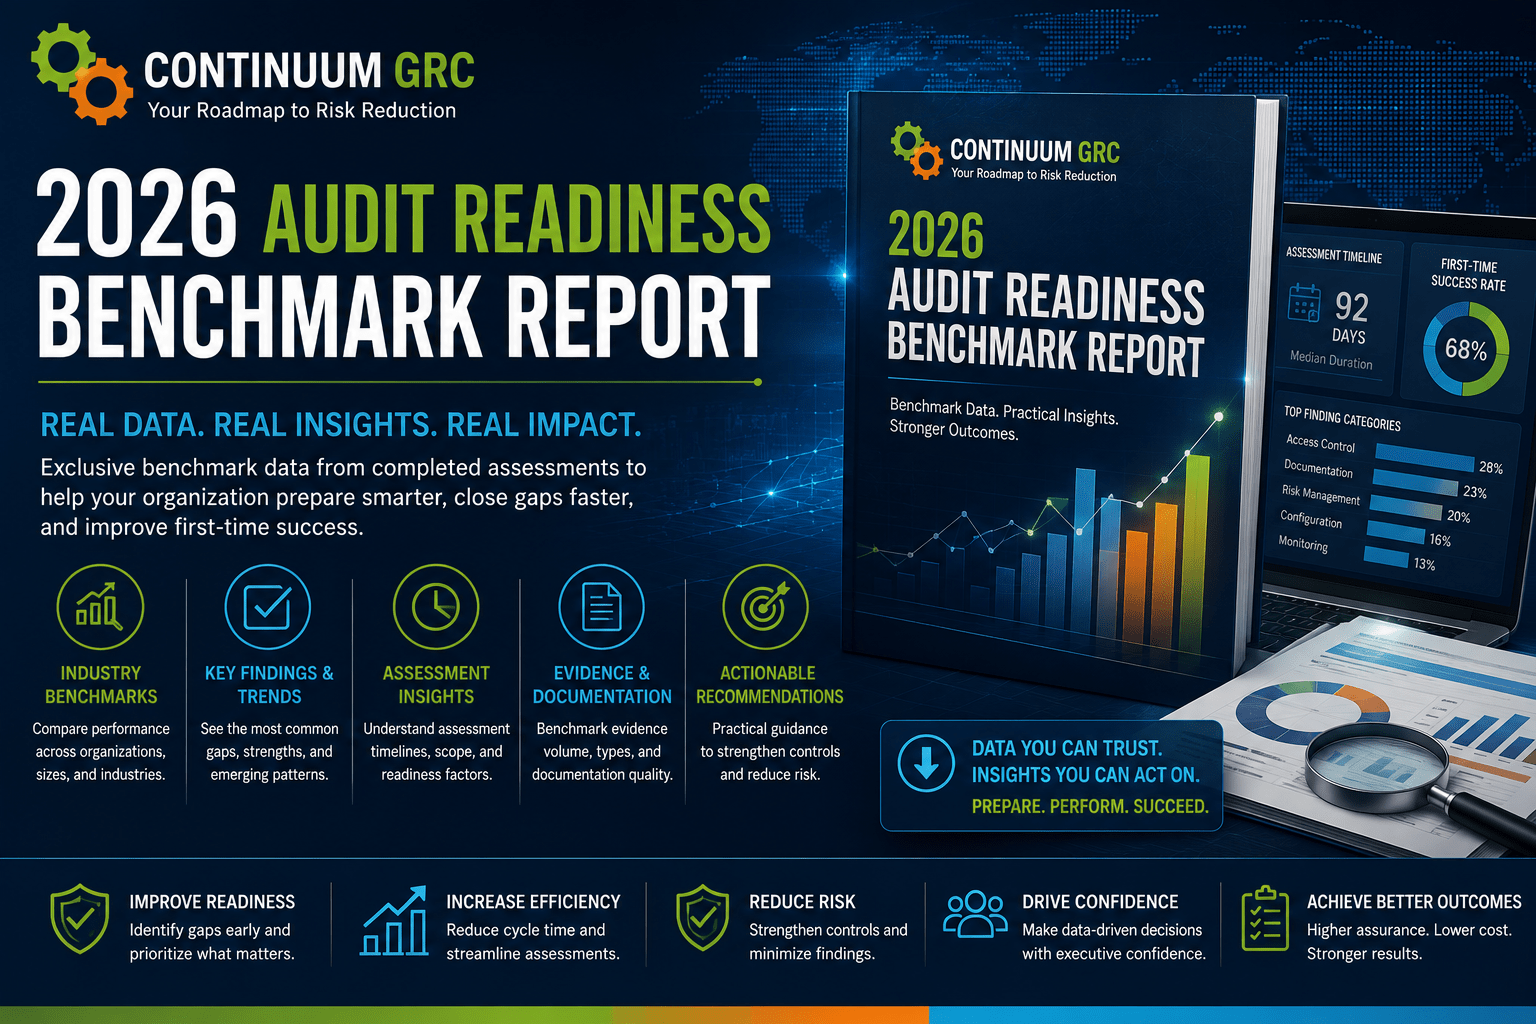
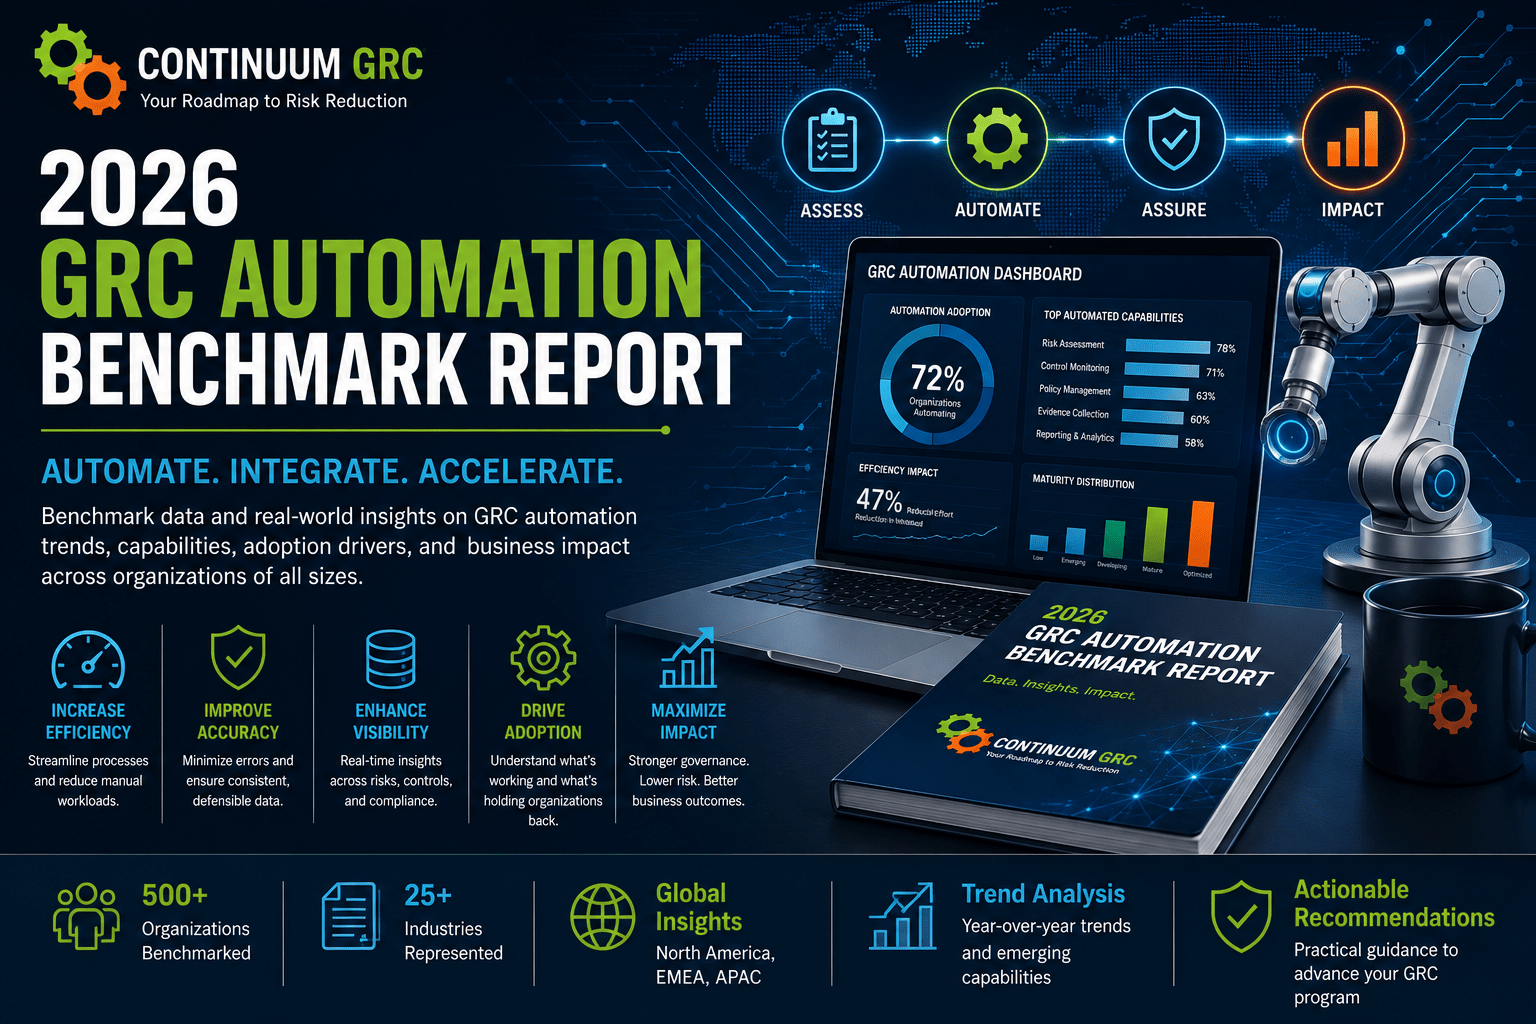
SOC 2 audits are no longer a static customer-assurance exercise. In 2026, buyers expect SOC 1 and SOC 2 reports to explain real cloud compliance boundaries, AI audit scoping decisions, subservice organization dependencies, risk management practices, and assurance reporting that executives can trust. The most successful organizations treat SOC reporting as an operating model: a reusable evidence engine that connects security, finance, privacy, AI governance, and customer assurance.
The practical shift is this: cloud and AI systems have made audit scope a business-risk decision, not a paperwork decision. A narrow SOC 2 scope may look efficient until a customer asks whether your generative AI workflow, managed cloud provider, data lake, support tooling, or model-training pipeline is actually covered.