6 HIPAA Cybersecurity Audit Wins with Continuum GRC

6 HIPAA Cybersecurity Audit Wins with Continuum GRC

HIPAA cybersecurity audit readiness is no longer a paperwork exercise. For covered entities and business associates, the decisive audit question is whether ePHI safeguards, risk analysis, risk management, and operational resilience work under pressure—not merely whether policies exist. Continuum GRC helps healthcare organizations turn HIPAA audit preparation into a defensible, evidence-driven cybersecurity program that withstands regulator scrutiny, customer due diligence, ransomware stress, and board-level risk review.

The emerging insight for 2026 is simple but uncomfortable: a HIPAA audit failure is often not caused by one missing control. It is caused by weak traceability between ePHI locations, threat scenarios, safeguards, evidence, risk decisions, and remediation ownership.
Read More

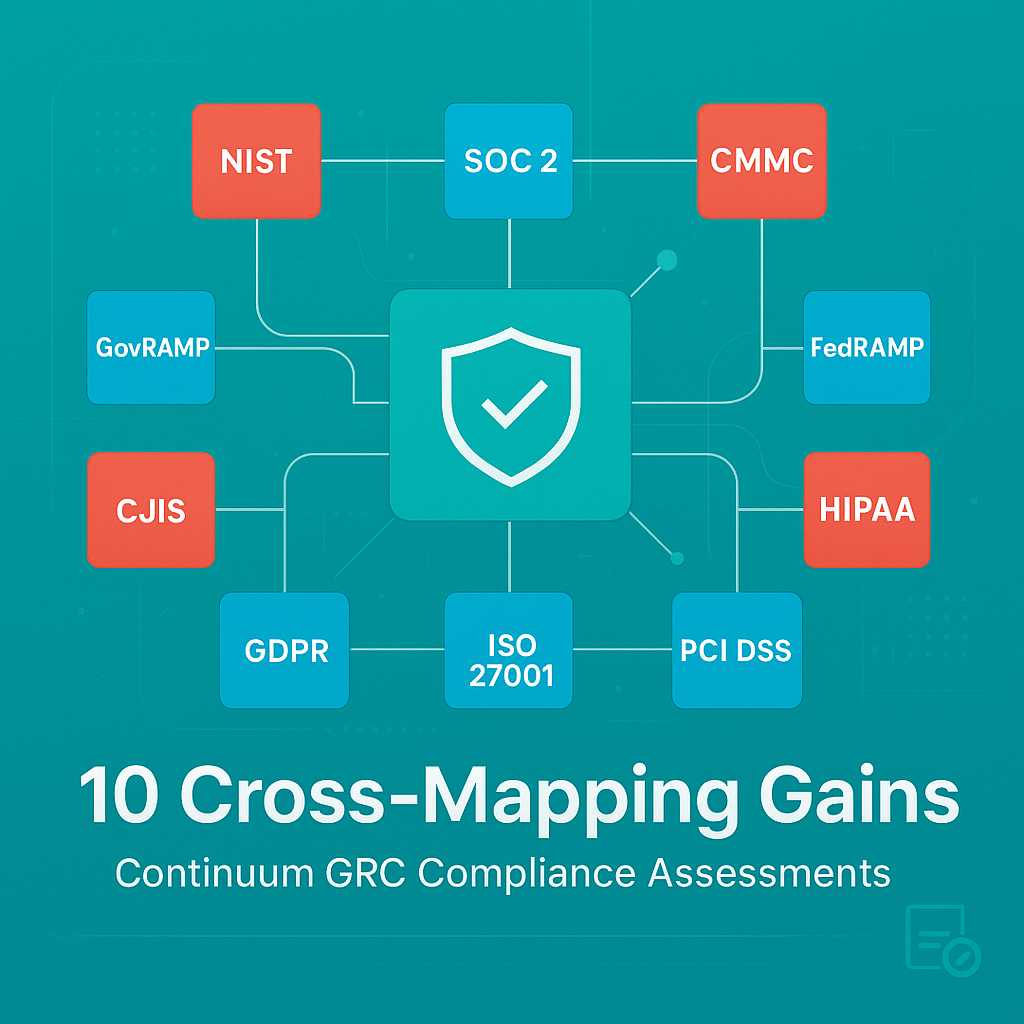
10 Cross-Mapping Gains with Continuum GRC Compliance Assessments

10 Cross-Mapping Gains with Continuum GRC Compliance Assessments

Cross-mapping is no longer a convenience feature for governance risk compliance teams; it is becoming the operating model for credible multi-framework compliance. In 2026, CISOs, compliance officers, and IT security leaders are expected to prove that one control environment can satisfy overlapping obligations across NIST 800-53, SOC 1, SOC 2, CMMC, DFARS/NIST 800-171, FedRAMP, GovRAMP, ISO 27001, HIPAA, PCI DSS, CJIS, C5, GDPR, CCPA, and LADMF without creating duplicative audit work.

The strategic advantage of Continuum GRC compliance assessments is the disciplined use of a unified control library: a normalized, evidence-driven structure that connects security objectives, mapped requirements, control owners, evidence artifacts, test procedures, risks, exceptions, and remediation plans. That is where cross-mapping changes from a spreadsheet exercise into an audit-ready compliance architecture.

Read More

10 SOC 2 AI Risk Controls with Continuum GRC for 2026

10 SOC 2 AI Risk Controls with Continuum GRC for 2026

SOC 2 audit readiness is changing in 2026 because AI risk controls, privacy compliance, operational resilience, risk management, and continuous monitoring are now part of the same assurance conversation. The practical issue is not whether an organization uses AI; it is whether AI use is governed inside the SOC 2 system boundary, monitored with evidence, and aligned to commitments made to customers, regulators, and boards.

Read More