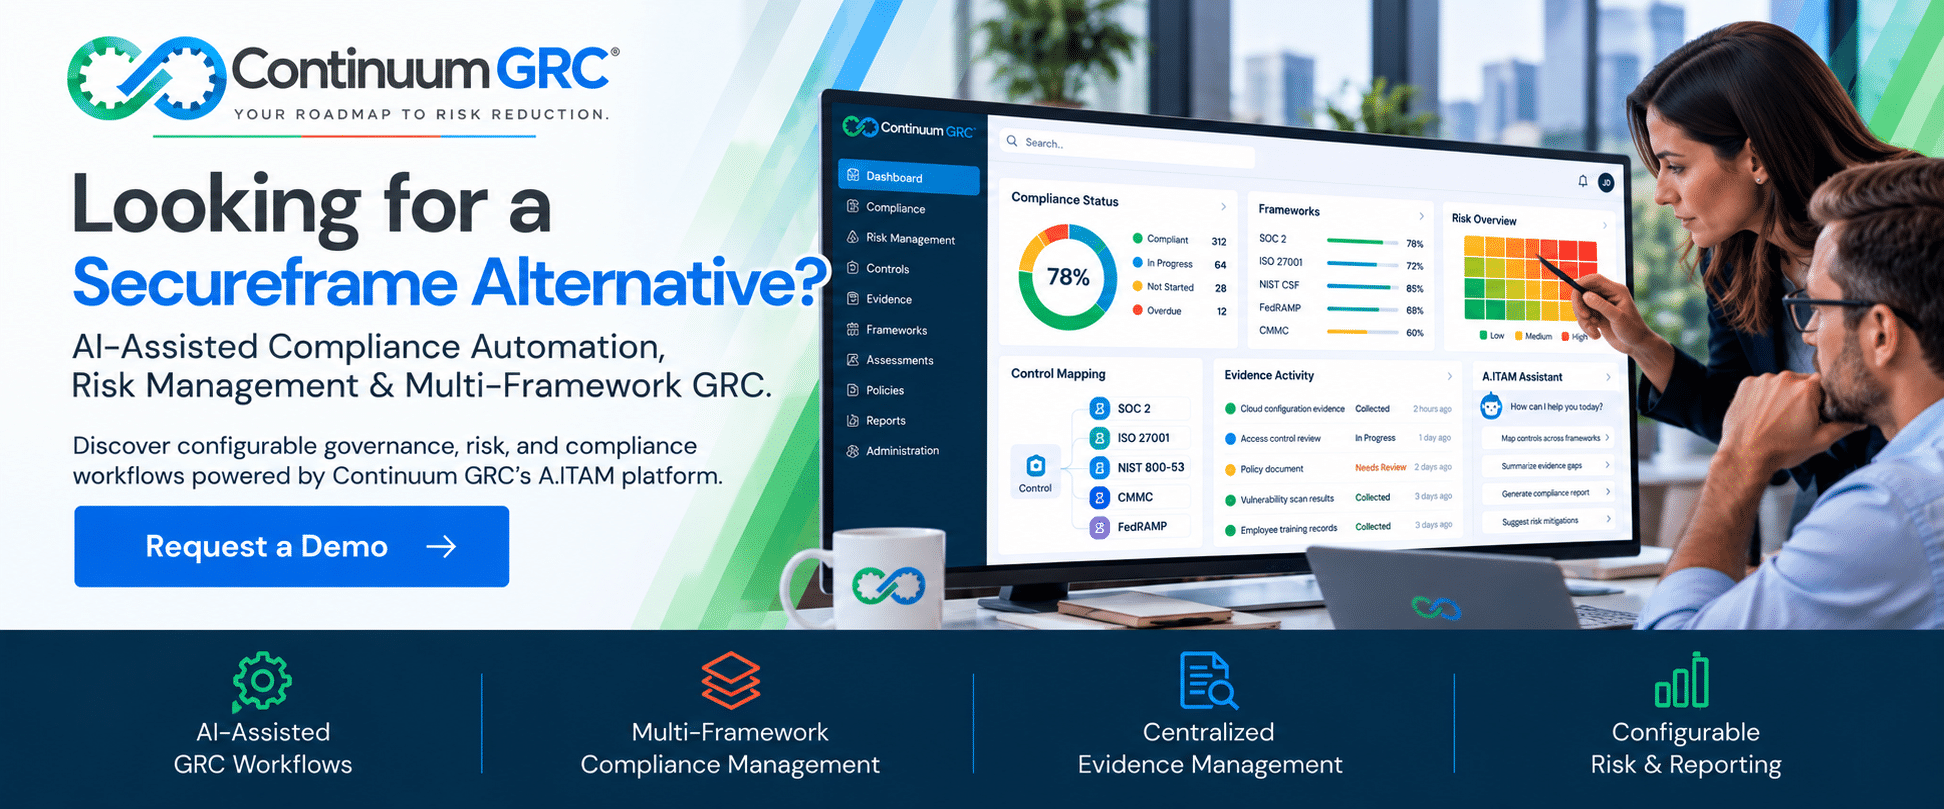
AI-Assisted Compliance Automation, Risk Management, and Multi-Framework GRC Software
Table of Contents
ToggleEvaluating Secureframe for SOC 2 compliance automation, ISO 27001 certification readiness, continuous control monitoring, or cybersecurity audit preparation?
Discover Continuum GRC, a configurable governance, risk, and compliance platform designed to help organizations manage security controls, organize evidence, assess risk, and coordinate regulatory compliance across multiple frameworks.
Powered by the A.ITAM™ platform, Continuum GRC combines compliance management, risk assessment, control mapping, audit documentation, reporting, and AI-assisted workflows in one centralized environment.
Whether your organization is implementing its first compliance program or coordinating complex requirements across multiple departments, Continuum GRC offers an alternative worth evaluating.
Why Consider Continuum GRC as an Alternative to Secureframe?
Secureframe offers compliance automation, continuous monitoring, evidence collection, risk management, and audit readiness capabilities.
Continuum GRC approaches these challenges through configurable GRC workflows, centralized compliance management, AI-assisted processes, and support for a broad range of regulatory frameworks.
The best platform depends on your organization's compliance requirements, technology environment, governance structure, and operational priorities.
1. Configurable Governance, Risk, and Compliance Management
Organizations often need more than standardized compliance checklists.
Continuum GRC supports configurable controls, assessments, questionnaires, documentation, workflows, and reporting structures that can be adapted to an organization's internal processes and regulatory obligations.
This flexibility is particularly valuable when compliance requirements span multiple business units, regulatory authorities, and assessment programs.
2. AI-Assisted Compliance With A.ITAM and AITAMBot
Continuum GRC incorporates AI-assisted functionality designed to support GRC teams with activities such as:
- Control analysis and mapping
- Compliance documentation
- Evidence organization and review
- Risk identification and assessment
- Audit preparation
- Regulatory requirement interpretation
- Reporting and workflow coordination
These capabilities help organizations explore opportunities to reduce repetitive administrative work while maintaining appropriate human review and accountability.
AI-generated recommendations and assessments should be independently validated before being relied upon for regulatory or assurance decisions.
3. Multi-Framework Compliance Management
Organizations rarely operate under only one compliance framework.
Continuum GRC supports programs involving:
- SOC 1, SOC 2, and SOC 3
- ISO/IEC 27001
- NIST Cybersecurity Framework
- NIST SP 800-53
- NIST SP 800-171
- FedRAMP
- CMMC
- HIPAA
- PCI DSS
- GDPR
- Other federal, industry, and international requirements
Centralized control management and cross-framework mapping can help teams identify overlapping requirements and opportunities to reuse appropriate evidence.
4. Federal and Defense Compliance Workflows
Organizations operating in government and defense markets may need to coordinate complex control requirements, assessment evidence, remediation activities, and reporting obligations.
Continuum GRC supports compliance management workflows related to FedRAMP, CMMC, NIST SP 800-53, and NIST SP 800-171.
Continuum GRC also offers a FedRAMP-authorized SaaS platform. Buyers should confirm that the proposed deployment and required services fall within the applicable authorization boundary.
Use of a GRC platform does not itself provide FedRAMP authorization, CMMC certification, or regulatory approval.
5. Centralized Evidence and Audit Management
Audit preparation often requires coordinating documentation across security, IT, operations, human resources, legal, and executive management.
Continuum GRC provides a centralized environment for organizing evidence, assigning responsibilities, tracking requirements, and preparing audit documentation.
This can help teams reduce fragmented spreadsheets and disconnected evidence repositories.
6. Integrated Risk Management
Compliance programs should be connected to operational and cybersecurity risk.
Continuum GRC supports risk registers, assessments, control relationships, remediation tracking, and management reporting.
This approach helps organizations move beyond individual audit projects toward broader governance and risk management processes.
7. Customizable Reporting and Workflows
Different organizations require different approval processes, evidence structures, reporting formats, and management dashboards.
Continuum GRC's configurable workflows and reporting capabilities support these varying needs.
When evaluating Secureframe and Continuum GRC, organizations should compare the specific configuration options, implementation requirements, and administrative effort associated with each platform.
Continuum GRC vs. Secureframe: Compare Compliance Automation Platforms
Looking for a Secureframe alternative? Compare Continuum GRC and Secureframe across AI-assisted compliance automation, SOC 2, ISO 27001, FedRAMP, CMMC, evidence management, risk management, integrations, and configurable GRC workflows.
| Evaluation Criteria | Continuum GRC | Secureframe |
|---|---|---|
| Primary Platform Focus | Configurable governance, risk, compliance, and audit management | Compliance automation, continuous monitoring, and audit readiness |
| AI-Assisted Compliance | ✓ A.ITAM and AITAMBot AI-assisted GRC workflows | AI-assisted compliance, evidence review, and security workflows |
| SOC 2 Compliance | ✓ Control management, evidence tracking, and audit preparation | SOC 2 automation, evidence collection, and audit readiness |
| ISO/IEC 27001 | ✓ ISMS controls, risk assessment, and evidence management | ISO 27001 automation, control monitoring, and certification preparation |
| NIST Cybersecurity Framework | ✓ NIST CSF controls, assessments, and reporting | NIST framework support; verify applicable version and requirements |
| NIST SP 800-53 | ✓ Federal security control and evidence management | NIST-related compliance capabilities; confirm detailed control coverage |
| NIST SP 800-171 | ✓ Defense cybersecurity controls and evidence | NIST-related compliance workflows; confirm supported requirements |
| FedRAMP Workflows | ✓ FedRAMP controls, evidence, and assessment management workflows | FedRAMP-related compliance support; verify program and pathway coverage |
| CMMC Workflows | ✓ CMMC controls, evidence, and remediation management | CMMC-related compliance capabilities; verify current framework coverage |
| Multi-Framework Mapping | ✓ Cross-framework control mapping and evidence reuse | Shared controls, common requirements, and framework mapping |
| Evidence Management | Centralized evidence, documentation, and compliance tracking | Centralized evidence management and automated collection |
| Automated Evidence Collection | Automation through supported integrations and configured workflows | Prebuilt integrations for automated evidence collection |
| Continuous Monitoring | Ongoing compliance tracking and configured monitoring workflows | Automated security and compliance monitoring |
| Risk Management | ✓ Risk registers, assessments, remediation, and reporting | Risk assessments, remediation, and compliance risk management |
| Vendor Risk Management | Configurable third-party assessments and workflows | Vendor risk assessments, questionnaires, and third-party monitoring |
| Policy Management | Policy documentation, control relationships, and compliance workflows | Policy management, templates, and compliance workflows |
| Custom GRC Workflows | ✓ Configurable questionnaires, controls, assessments, and workflows | Configurable controls and compliance workflows; verify plan-level options |
| Audit Management | Audit preparation, evidence coordination, assessments, and reporting | Audit readiness, auditor collaboration, and evidence sharing |
| Dashboards and Reporting | Customizable risk, compliance, and assessment dashboards | Compliance dashboards, control status, and audit reporting |
| Integrations and APIs | API connectivity and supported integration options | Broad prebuilt integration ecosystem and API capabilities |
| FedRAMP-Authorized SaaS | ✓ FedRAMP-authorized platform; confirm applicable authorization boundary | Confirm current authorization status for the proposed service and deployment |
| Implementation | Configuration based on modules, frameworks, workflows, and organizational requirements | Implementation based on integrations, frameworks, automation, and selected plan |
| Subscription Pricing | Modular subscriptions and tailored proposals | Subscription pricing based on plan, scope, and requirements |
| Total Cost of Ownership | Evaluate subscription, modules, implementation, integrations, and support | Evaluate subscription, plan features, integrations, implementation, and support |
| Primary Evaluation Fit | Organizations seeking configurable, multi-framework GRC, risk management, and AI-assisted workflows | Organizations prioritizing automated evidence collection, integrations, and continuous compliance monitoring |
Comparison disclaimer: This comparison is provided for informational purposes only. Both platforms offer overlapping compliance automation and GRC capabilities. Features may vary by subscription, implementation, configuration, and integration. Verify current capabilities, security qualifications, authorization boundaries, and pricing directly with each vendor. Using compliance software does not itself constitute certification, regulatory compliance, or authorization. Continuum GRC is not affiliated with, sponsored by, or endorsed by Secureframe.
When Continuum GRC May Be a Better Fit
Your Organization Manages Multiple Regulatory Frameworks
Continuum GRC may be worth evaluating when compliance requirements extend beyond SOC 2 or ISO 27001 to include federal, defense, privacy, and industry-specific programs.
You Need Custom GRC Workflows
Organizations with complex approval structures, internal governance processes, or unique regulatory obligations should evaluate Continuum GRC's configurable controls, questionnaires, and workflows.
You Want to Connect Compliance and Risk Management
Continuum GRC supports an integrated approach to compliance controls, risk registers, remediation activities, and management reporting.
You Need Federal Compliance Management
Organizations subject to FedRAMP, CMMC, NIST SP 800-53, or NIST SP 800-171 requirements can evaluate Continuum GRC's federal compliance workflows and applicable hosting options.
You Want to Evaluate AI-Assisted GRC
Continuum GRC's A.ITAM and AITAMBot capabilities provide an opportunity to explore AI-assisted compliance analysis, control mapping, evidence management, and reporting.
You Want to Compare Total Cost of Ownership
When evaluating Secureframe and Continuum GRC, compare subscription fees, implementation, required modules, integrations, administrative effort, support, and ongoing maintenance.
The lowest subscription price is not necessarily the lowest overall operating cost.
Considering a Move From Secureframe to Continuum GRC?
Organizations may consider changing compliance platforms when their regulatory requirements expand, their governance needs become more complex, or they want to evaluate alternative automation and reporting capabilities.
A migration assessment should review:
- Existing frameworks and control libraries
- Historical audit evidence and retention requirements
- Integration dependencies
- Risk registers and remediation records
- Policy and approval workflows
- Current reporting requirements
- Data export and import capabilities
- Security and privacy requirements
- Training and implementation effort
- Parallel operation and cutover planning
Not every integration, automation, or data structure will transfer directly between platforms.
Frequently Asked Questions About Secureframe Alternatives
What is a good alternative to Secureframe?
Continuum GRC is an option for organizations seeking configurable compliance management, risk assessment, evidence organization, multi-framework support, and AI-assisted GRC workflows.
Other alternatives include Drata, Vanta, Hyperproof, and enterprise GRC platforms.
How does Continuum GRC compare with Secureframe?
Continuum GRC emphasizes configurable GRC workflows, multi-framework compliance management, risk assessment, and A.ITAM AI-assisted capabilities.
Secureframe emphasizes compliance automation, integrations, evidence collection, and ongoing security monitoring.
Both platforms offer overlapping functionality, making a requirements-based demonstration important.
Does Continuum GRC support SOC 2?
Yes. Continuum GRC supports SOC 2-related control management, documentation, evidence tracking, and audit preparation.
An independent CPA firm must perform the SOC examination and issue the applicable report.
Can Continuum GRC help with ISO 27001?
Yes. Continuum GRC supports ISO/IEC 27001 control management, risk assessment, documentation, and evidence organization.
Certification requires a separate certification process conducted by an appropriately qualified certification body.
Does Continuum GRC support FedRAMP?
Continuum GRC supports FedRAMP-related control management, evidence organization, and compliance workflows.
The platform's FedRAMP authorization is distinct from a customer's authorization requirements.
Can Continuum GRC help with CMMC?
Yes. Continuum GRC can support CMMC-related controls, documentation, and evidence management.
Using the platform does not constitute CMMC certification.
Does Secureframe offer AI capabilities?
Yes. Secureframe offers AI-assisted compliance and security functionality.
Organizations should compare the specific capabilities, accuracy, oversight, and subscription requirements of each platform.
Does Continuum GRC automate evidence management?
Continuum GRC supports centralized evidence management and automation through supported workflows and integrations.
Buyers should verify their specific evidence collection requirements during a demonstration.
Does Continuum GRC offer risk management?
Yes. Continuum GRC supports risk assessments, risk registers, control relationships, remediation tracking, and reporting.
Can Continuum GRC replace Secureframe?
Potentially. Suitability depends on existing integrations, compliance frameworks, evidence requirements, workflow needs, and migration complexity.
A structured requirements review and proof of concept are recommended before changing platforms.
How much does Continuum GRC cost compared with Secureframe?
Costs depend on subscription scope, modules, users, implementation, integrations, and contractual terms.
Request comparable proposals to evaluate total cost of ownership.
Is Continuum GRC suitable for enterprise organizations?
Continuum GRC supports configurable governance, risk, and compliance workflows that can accommodate complex requirements.
Enterprise buyers should validate scalability, access controls, reporting, security, integrations, and support against their own requirements.
Discover a Secureframe Alternative Built for Broader GRC Management
Your organization needs a sustainable approach to governance, risk, and compliance—not simply a collection of audit checklists.
Continuum GRC helps teams organize regulatory requirements, coordinate audit evidence, manage risk, and maintain configurable compliance workflows.
Powered by A.ITAM and AI-assisted capabilities, Continuum GRC offers an alternative for organizations evaluating how to manage compliance across multiple frameworks.
See How Continuum GRC Fits Your Requirements
Contact us using the form below or calling us at 1-888-896-6207 for assistance.
Continuum GRC is not affiliated with, sponsored by, or endorsed by Secureframe. Secureframe is a trademark of its respective owner. Product comparisons are provided for informational purposes and should be validated against current vendor documentation and demonstrations.