DFARS Compliance Automation & NIST SP 800-171 Management
Table of Contents
ToggleSimplify DFARS cybersecurity compliance with automated NIST SP 800-171 control management, evidence collection, SPRS assessment readiness, System Security Plans, POA&M tracking, and CMMC-aligned workflows—all within Continuum GRC's FedRAMP Authorized GRC platform.
Continuum GRC helps organizations manage applicable DFARS cybersecurity requirements in one centralized platform. Connect NIST SP 800-171 security requirements with implementation documentation, assessment evidence, corrective actions, and continuous monitoring.
From initial readiness through recurring assessments, Continuum GRC provides a structured roadmap for managing cybersecurity obligations across the Defense Industrial Base.
Built for Defense Contractors and the Defense Industrial Base
Department of Defense contractors and subcontractors must navigate overlapping cybersecurity requirements involving Controlled Unclassified Information (CUI), covered contractor information systems, NIST SP 800-171, DFARS contract clauses, and applicable CMMC requirements.
Continuum GRC helps organizations translate these obligations into manageable compliance activities by centralizing security controls, control ownership, implementation status, assessment evidence, findings, and remediation.
The platform supports defense contractors seeking to:
- Establish and maintain NIST SP 800-171 control implementations.
- Prepare for applicable DoD cybersecurity assessments.
- Maintain System Security Plans and Plans of Action and Milestones.
- Organize evidence supporting SPRS assessment results.
- Identify and remediate security deficiencies.
- Reuse relevant documentation across DFARS and CMMC workflows.
- Monitor security control performance over time.
Continuum GRC provides compliance management and assessment preparation capabilities. It does not independently confer DFARS compliance status, determine government assessment outcomes, or issue CMMC certifications.
Understanding DFARS Cybersecurity Requirements
DFARS cybersecurity obligations extend beyond a single security framework. Depending on the contract, contractors may need to implement NIST SP 800-171 security requirements, maintain current assessment results, report covered cyber incidents, and satisfy applicable CMMC status requirements.
Continuum GRC helps organizations organize these obligations and maintain the documentation, evidence, and corrective-action records needed to support compliance activities.
| Requirement | What It Addresses | Continuum GRC Support |
|---|---|---|
| DFARS 252.204-7012 | Safeguarding covered defense information and reporting covered cyber incidents. | Security control management, evidence documentation, and incident-response workflows. |
| DFARS 252.204-7019 | Notice of NIST SP 800-171 DoD assessment requirements, including applicable assessment information in SPRS. | Assessment readiness, supporting documentation, and evidence management. |
| DFARS 252.204-7020 | DoD NIST SP 800-171 assessment requirements, including applicable assessment access and cooperation. | Assessment preparation, scoring support, evidence organization, and remediation tracking. |
| DFARS 252.204-7021 | Applicable Cybersecurity Maturity Model Certification (CMMC) level and status requirements. | CMMC compliance management , control mapping, assessment readiness, and evidence reuse. |
| NIST SP 800-171 | Security requirements for protecting Controlled Unclassified Information (CUI) in covered nonfederal systems. | Security control mapping, System Security Plans (SSPs), implementation documentation, and assessment evidence. |
| NIST SP 800-172 | Enhanced security requirements for protecting CUI against advanced persistent threats, where applicable. | Enhanced control mapping, assessment documentation, and supporting evidence management. |
Important: Requirements depend on the clauses incorporated into the applicable DoD contract. NIST SP 800-172 is not universally required for all defense contractors. Continuum GRC supports compliance management and assessment preparation but does not independently confer certification or government assessment status.
SPRS Assessment Readiness & NIST SP 800-171 Scoring
The Supplier Performance Risk System (SPRS) is used by the Department of Defense to maintain cybersecurity assessment information associated with applicable contractor systems.
Continuum GRC helps organizations prepare for NIST SP 800-171 assessments by maintaining the underlying control implementation records, assessment evidence, findings, and corrective actions supporting their reported results.
Key capabilities
- Organize applicable NIST SP 800-171 assessment requirements.
- Support assessment scoring using the applicable DoD assessment methodology.
- Identify unmet requirements and potential scoring impacts.
- Maintain supporting evidence and implementation statements.
- Track assessment scope, dates, and remediation.
- Prepare supporting records for SPRS reporting.
- Monitor changes that may affect assessment results.
Continuum GRC supports SPRS assessment preparation and internal recordkeeping. Official assessment results and SPRS submissions remain subject to the applicable DoD procedures and authorized responsibilities.
Automated DFARS & NIST SP 800-171 Evidence Collection
Defense contractors frequently maintain security evidence across cloud infrastructure, identity platforms, endpoint security tools, ticketing systems, document repositories, and internal business applications.
Continuum GRC helps centralize evidence collection and management through supported APIs, integrations, webhooks, document repositories, and automated workflows.
Evidence can be associated with applicable security requirements, implementation statements, assessment activities, findings, and remediation actions.
From Requirements to Continuous Monitoring
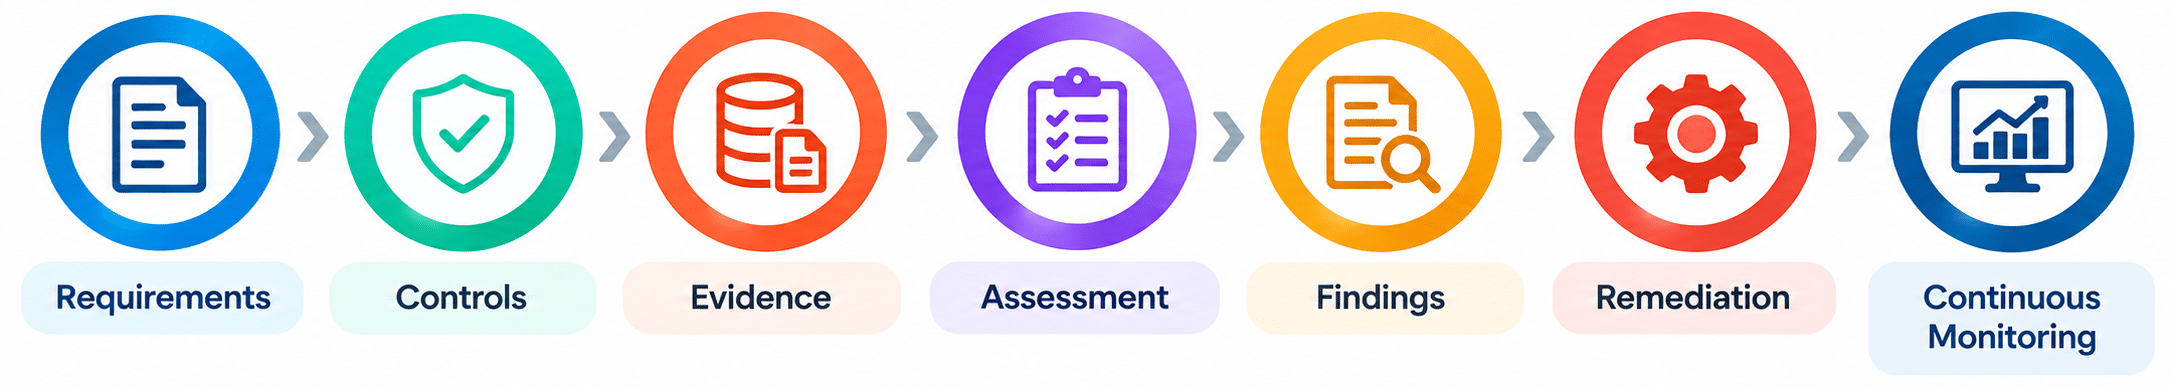
By connecting these activities, organizations can reduce repetitive evidence collection, identify documentation gaps, and maintain better visibility into compliance readiness.
DFARS System Security Plans, Assessment Reports & POA&M Management
Continuum GRC provides integrated workflows for organizing the documentation and corrective actions associated with NIST SP 800-171 compliance.
System Security Plans (SSPs)
Maintain system boundaries, security requirement implementation statements, responsible personnel, supporting documentation, and control status.
Security Assessment Reports (SARs)
Organize assessment procedures, testing results, observations, supporting evidence, and identified deficiencies.
Plans of Action and Milestones (POA&Ms)
Track deficiencies, remediation owners, corrective actions, target dates, supporting evidence, and closure activities.
Together, these capabilities provide a structured compliance record that can be maintained as systems, requirements, and assessment conditions change.
POA&Ms do not automatically satisfy unmet contractual requirements. Their acceptability depends on the applicable DFARS, assessment, and CMMC rules.
DFARS Compliance and CMMC Assessment Readiness
DFARS and CMMC share important cybersecurity requirements, but they serve different purposes.
DFARS clauses establish contractual cybersecurity and assessment obligations. CMMC establishes applicable cybersecurity assessment and status requirements for covered DoD contracts.
Continuum GRC helps organizations manage common NIST SP 800-171 controls, supporting evidence, implementation documentation, and remediation records across both programs.
Cross-framework evidence reuse can reduce duplicative compliance work while maintaining the distinct documentation, assessment, and certification requirements of each program.
An SPRS score does not constitute CMMC certification, and use of Continuum GRC does not replace an authorized CMMC assessment.
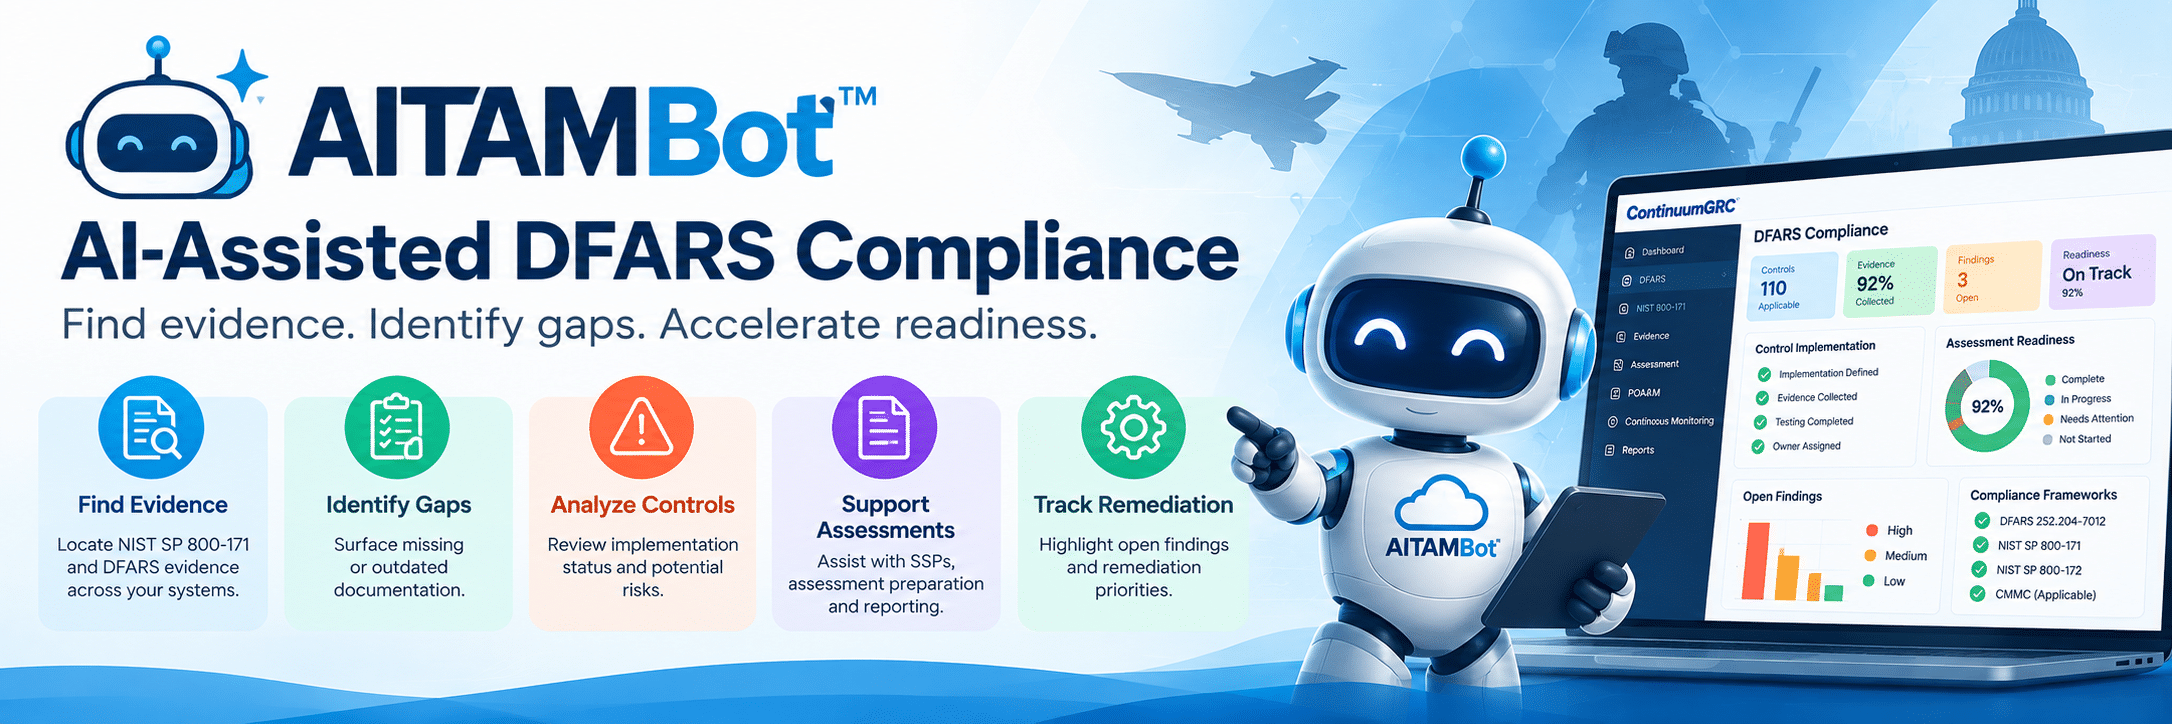
AI-Assisted DFARS Compliance with AITAMBot™
AITAMBot™ helps defense contractors reduce repetitive compliance preparation and review activities through AI-assisted analysis of security controls, evidence, assessment information, and remediation records.
AITAMBot can help compliance teams:
- Locate NIST SP 800-171 evidence.
- Identify missing or outdated documentation.
- Surface requirements requiring additional review.
- Analyze implementation information for potential gaps.
- Identify open findings and remediation priorities.
- Support SSP and assessment documentation preparation.
- Assist with readiness reporting and compliance dashboards.
- Answer natural-language questions about available compliance information.
AITAMBot™ works alongside compliance professionals and assessors rather than replacing required independent judgment, DoD assessment authority, or CMMC certification assessments.
DFARS Assessment, Documentation & Continuous Monitoring Modules
Continuum GRC provides configurable DFARS and NIST assessment modules supporting System Security Plans, Security Assessment Reports, NIST SP 800-171 and NIST SP 800-172 documentation, FIPS 199 categorization, Plans of Action and Milestones, and recurring compliance monitoring.
These modules are part of Continuum GRC's broader library of 100+ supported compliance frameworks, enabling organizations to reuse applicable controls and evidence across overlapping security obligations.
- DFARS NIST 800-171 System Security Plan (SSP)
- DFARS NIST 800-171 Security Assessment Report (SAR)
- DFARS NIST 800-172 System Security Plan (SSP)
- DFARS NIST 800-172 Security Assessment Report (SAR)
- Federal Information Processing Standard (FIPS) 199 Categorization
- Plan of Action and Milestones (POA&M)
DFARS & NIST SP 800-171 Compliance Platform Comparison – 2026
Compare compliance automation capabilities relevant to DFARS cybersecurity requirements, NIST SP 800-171, SPRS assessment readiness, CMMC alignment, evidence management, and continuous monitoring.
| Feature | Continuum GRC | Drata | Secureframe | Vanta | PreVeil |
|---|---|---|---|---|---|
| Platform & Framework Capabilities | |||||
| FedRAMP Authorized SaaS Platform | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| DFARS & NIST SP 800-171 Compliance Management | ✓ Yes | Supported | Supported | Supported | Supported |
| NIST SP 800-171 Control Mapping | ✓ Yes | Supported | Supported | Supported | Supported |
| NIST SP 800-172 Enhanced Requirements | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| Custom Framework Creation | ✓ Yes | Supported | Supported | Supported | Not publicly confirmed |
| Compliance Framework Library | 100+ Frameworks | Multiple Frameworks | Multiple Frameworks | Multiple Frameworks | CMMC / NIST Focus |
| Assessment Readiness & Documentation | |||||
| SPRS Assessment Scoring Support | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| System Security Plan (SSP) Management | ✓ Yes | Verify current offering | Supported | Verify current offering | Supported |
| Security Assessment Report (SAR) Documentation | ✓ Yes | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed | Not publicly confirmed |
| POA&M Management & Remediation Tracking | ✓ Yes | Supported | Supported | Supported | Supported |
| CMMC Assessment Readiness & Evidence Reuse | ✓ Yes | Supported | Supported | Supported | Supported |
| Independent Assessment Services Available | Through Lazarus Alliance | Verify partner options | Verify partner options | Verify partner options | Verify partner options |
| Evidence Automation & Monitoring | |||||
| Automated Evidence Collection | ✓ Yes | Supported | Supported | Supported | Supported |
| Continuous Monitoring & Alerts | ✓ Yes | Supported | Supported | Supported | Verify current offering |
| Control Implementation Tracking | ✓ Yes | Supported | Supported | Supported | Supported |
| Cross-Framework Evidence Reuse | ✓ Yes | Supported | Supported | Supported | Verify current offering |
| Real-Time Compliance Dashboards | ✓ Yes | Supported | Supported | Supported | Supported |
| Artificial Intelligence & Readiness Tools | |||||
| AI-Assisted Compliance Analysis | ✓ AITAMBot™ | Drata AI | Secureframe AI | Vanta AI | Verify current offering |
| Dedicated AI Auditor Tool | ✓ AITAMBot™ | Not directly comparable | Not directly comparable | Not directly comparable | Not publicly confirmed |
| Built-In Compliance Templates & Policies | ✓ Yes | Supported | Supported | Supported | Supported |
| Free 14-Day Trial Without Credit Card | ✓ Yes | Verify current terms | Verify current terms | Verify current terms | Verify current terms |
| Free DFARS / NIST SP 800-171 Readiness Tools | ✓ Free Compliance Tools | Verify current offering | Verify current offering | Verify current offering | Verify current offering |
Comparison notes: Features and availability may vary by subscription, implementation, service scope, and product updates. "Not publicly confirmed" means that the specific capability has not been verified for this comparison; it does not mean the vendor lacks the capability. Continuum GRC is a compliance management platform. Independent assessments, where applicable, are separate professional services and do not constitute automatic certification or government authorization. AITAMBot™ supports compliance professionals and does not replace required independent assessors.
Why Choose Continuum GRC for DFARS Compliance?
Centralized Compliance Management: Connect DFARS requirements, NIST SP 800-171 controls, responsible personnel, assessment results, and remediation records.
Automated Evidence Management: Reduce repetitive evidence collection through supported integrations, repositories, and configurable workflows.
Assessment Readiness: Maintain organized documentation supporting NIST SP 800-171 assessments and SPRS reporting.
SSP & POA&M Management: Keep security plans, findings, corrective actions, and supporting evidence aligned with ongoing compliance activities.
CMMC-Aligned Workflows: Reuse applicable controls and evidence while maintaining separate assessment and certification obligations.
AI-Assisted Compliance: Use AITAMBot™ to support evidence review, documentation analysis, and readiness reporting.
Continuous Monitoring: Track changes, recurring control activities, open findings, and remediation progress.
FedRAMP Authorized SaaS: Manage compliance activities using Continuum GRC's FedRAMP Authorized SaaS offering, subject to its documented authorization boundary and applicable customer responsibilities.
Frequently Asked Questions
What is DFARS cybersecurity compliance?
DFARS cybersecurity compliance refers to satisfying applicable cybersecurity requirements incorporated into Department of Defense contracts. These may include safeguarding covered defense information, implementing NIST SP 800-171 requirements, reporting covered cyber incidents, and meeting applicable assessment and CMMC obligations.
Is DFARS a cybersecurity certification?
No. DFARS is a supplement to federal acquisition regulations. Contractors must satisfy the requirements of applicable contract clauses, but there is no standalone DFARS certification.
What is the relationship between DFARS and NIST SP 800-171?
DFARS 252.204-7012 incorporates NIST SP 800-171 safeguarding requirements for covered contractor information systems, subject to the clause's applicable provisions. NIST SP 800-171 provides security requirements for protecting CUI in nonfederal systems and organizations.
What is an SPRS assessment score?
An SPRS assessment score is a result associated with the applicable DoD NIST SP 800-171 assessment methodology. The score reflects assessed implementation of applicable security requirements and is subject to the relevant reporting and assessment procedures.
Does Continuum GRC support SPRS scoring?
Continuum GRC supports NIST SP 800-171 assessment preparation, control tracking, findings management, and documentation used in scoring workflows. Official scoring and submission must follow the applicable DoD methodology and authorized processes.
Is DFARS compliance the same as CMMC certification?
No. DFARS establishes contractual obligations, while CMMC establishes assessment and status requirements for applicable DoD contracts. Shared NIST SP 800-171 evidence can support both programs, but an SPRS score does not replace required CMMC certification.
Does DFARS require a third-party assessment?
Not every DFARS-covered contractor is required to undergo the same assessment. Requirements depend on the applicable clauses, assessment level, and contract. Some DoD assessments are government-conducted, while applicable CMMC requirements may involve independent assessment organizations.
What is a System Security Plan?
An SSP documents the covered system, its boundaries, operating environment, applicable security requirements, and how those requirements are implemented.
What is a POA&M?
A Plan of Action and Milestones records identified deficiencies and planned corrective actions, including responsible parties and target completion dates. Its use does not automatically excuse unmet contractual requirements.
Does DFARS require cyber incident reporting within 72 hours?
DFARS 252.204-7012 requires contractors to rapidly report covered cyber incidents within 72 hours of discovery, subject to the clause's applicable requirements.
Does every defense contractor need NIST SP 800-172?
No. NIST SP 800-172 contains enhanced security requirements and is not universally applicable to all DFARS contractors.
Can CMMC evidence be reused for DFARS compliance?
Yes, where the same requirements, systems, scope, and assessment periods apply. Evidence reuse should preserve the distinct obligations and reporting requirements of each program.
How does AITAMBot™ support DFARS compliance?
AITAMBot™ assists with locating evidence, analyzing documentation, identifying potential gaps, reviewing findings, and supporting compliance reporting. Human review remains necessary.
How long does DFARS compliance take?
The timeline depends on the organization's system scope, existing controls, documentation quality, remediation needs, and applicable contractual requirements. There is no universal compliance timeline.
How does Continuum GRC support ongoing DFARS compliance?
Continuum GRC centralizes controls, evidence, assessments, corrective actions, ownership, and monitoring activities so organizations can maintain and review their compliance records as systems and requirements change.
Contact us using the form below or calling us at 1-888-896-6207 for assistance.